
Fortinet
NSE4_FGT-7.0 · Question #92
Examine this output from a debug flow: Why did the FortiGate drop the packet?
The correct answer is D. It matched the default implicit firewall policy. https://kb.fortinet.com/kb/documentLink.do?externalID=13900
Troubleshooting and Monitoring
Question
Examine this output from a debug flow:
Why did the FortiGate drop the packet?
Exhibit
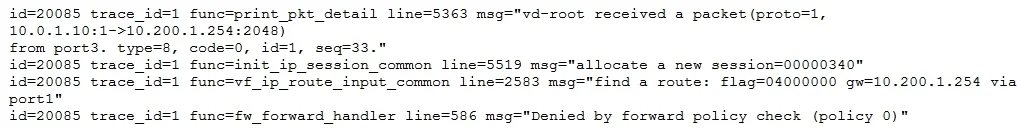
Options
- AThe next-hop IP address is unreachable.
- BIt failed the RPF check.
- CIt matched an explicitly configured firewall policy with the action DENY.
- DIt matched the default implicit firewall policy.
How the community answered
(20 responses)- A5% (1)
- B10% (2)
- C5% (1)
- D80% (16)
Explanation
Topics
#debug flow#packet drop#firewall policy#troubleshooting
Community Discussion
No community discussion yet for this question.