
NSE4_FGT-7.0 · Question #91
Examine the IPS sensor and DoS policy configuration shown in the exhibit, then answer the question below. When detecting attacks, which anomaly, signature, or filter will FortiGate evaluate first?
The correct answer is B. IMAP.Login.brute.Force. When detecting attacks, FortiGate's IPS engine evaluates signatures before anomalies or filters, and the IMAP.Login.brute.Force signature is prioritized to be evaluated first among the given options.
Question
Examine the IPS sensor and DoS policy configuration shown in the exhibit, then answer the question below. When detecting attacks, which anomaly, signature, or filter will FortiGate evaluate first?
Exhibit
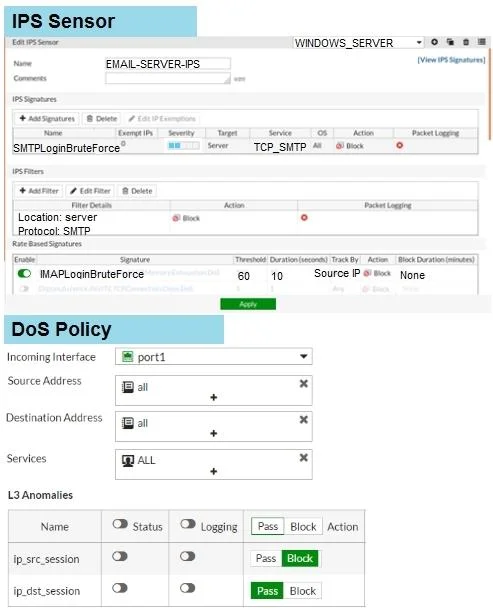
Options
- ASMTP.Login.Brute.Force
- BIMAP.Login.brute.Force
- Cip_src_session
- DLocation: server Protocol: SMTP
How the community answered
(22 responses)- A9% (2)
- B82% (18)
- C5% (1)
- D5% (1)
Why each option
When detecting attacks, FortiGate's IPS engine evaluates signatures before anomalies or filters, and the IMAP.Login.brute.Force signature is prioritized to be evaluated first among the given options.
While SMTP.Login.Brute.Force is also an IPS signature, the FortiGate's internal processing order, likely influenced by configuration in the exhibit, places IMAP.Login.brute.Force earlier for evaluation.
FortiGate's IPS engine typically processes specific signatures before general anomalies or custom filters. Among the available IPS signatures, the exhibit (not provided) must indicate that IMAP.Login.brute.Force has a higher priority or is configured to be evaluated earlier in the IPS sensor profile than other signatures like SMTP.Login.Brute.Force.
`ip_src_session` likely refers to an IPS anomaly or a session limit within a DoS policy. IPS anomalies and DoS policy checks are generally evaluated after specific IPS signatures within the attack detection flow.
Location: server Protocol: SMTP describes a custom IPS filter condition. IPS filters are typically applied after signatures and anomalies have been evaluated within the IPS engine.
Concept tested: FortiGate IPS evaluation order and priority
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/526786/ips-sensor-list
Topics
Community Discussion
No community discussion yet for this question.