
NSE4_FGT-7.0 · Question #82
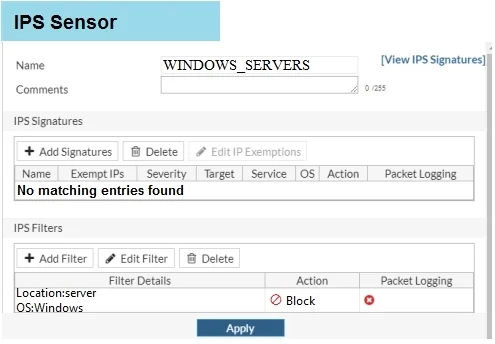
Examine the IPS sensor configuration shown in the exhibit, and then answer the question below. An administrator has configured the WINDOWS_SERVERS IPS sensor in an attempt to determine whether the…
The correct answer is E. The firewall policy is not using a full SSL inspection profile. If a FortiGate IPS sensor is not generating logs for HTTPS traffic, the most probable reason is that the firewall policy is not using a full SSL inspection profile, preventing the IPS from decrypting and inspecting the encrypted payload.
Question
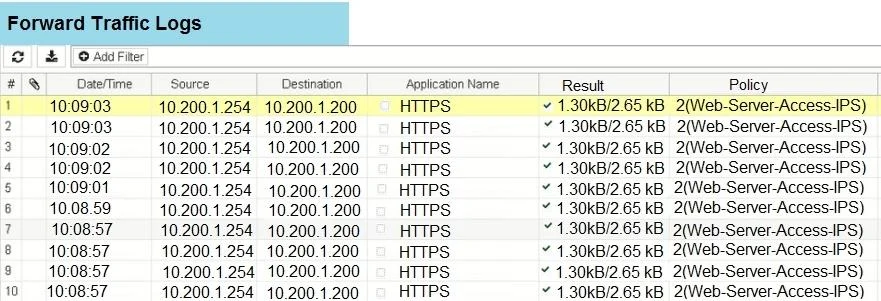
Examine the IPS sensor configuration shown in the exhibit, and then answer the question below. An administrator has configured the WINDOWS_SERVERS IPS sensor in an attempt to determine whether the influx of HTTPS traffic is an attack attempt or not. After applying the IPS sensor, FortiGate is still not generating any IPS logs for the HTTPS traffic. What is a possible reason for this?
Exhibits
Options
- AThe IPS filter is missing the Protocol: HTTPS option.
- BThe HTTPS signatures have not been added to the sensor.
- CA DoS policy should be used, instead of an IPS sensor.
- DA DoS policy should be used, instead of an IPS sensor.
- EThe firewall policy is not using a full SSL inspection profile.
How the community answered
(55 responses)- A18% (10)
- B11% (6)
- C2% (1)
- D4% (2)
- E65% (36)
Why each option
If a FortiGate IPS sensor is not generating logs for HTTPS traffic, the most probable reason is that the firewall policy is not using a full SSL inspection profile, preventing the IPS from decrypting and inspecting the encrypted payload.
While IPS sensors can have filters, the absence of a 'Protocol: HTTPS' option in an IPS filter is not typically the primary reason for IPS failing to log any attack attempts within HTTPS traffic. IPS generally inspects based on signatures, not a global protocol switch.
Although the absence of relevant HTTPS signatures would prevent specific attack detection, the more fundamental issue preventing any IPS logging for HTTPS traffic is the inability to decrypt the traffic for inspection, which full SSL inspection provides.
A DoS policy is designed to mitigate denial of service attacks by rate-limiting or blocking excessive traffic, which is a different function than an IPS sensor's role of detecting and preventing exploit attempts or malicious content within the traffic payload.
For the FortiGate IPS engine to effectively inspect the content within encrypted HTTPS traffic for attack attempts, it must be able to decrypt the traffic. If the firewall policy handling this HTTPS traffic is not configured to use a 'Full SSL inspection' profile, the traffic remains encrypted, and the IPS sensor cannot inspect the payload, thus not generating any logs for potential threats within it.
Concept tested: IPS inspection of encrypted HTTPS traffic and SSL inspection
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/607542/ssl-inspection-for-ips
Topics
Community Discussion
No community discussion yet for this question.