
NSE4_FGT-7.0 · Question #64
Refer to the web filter raw logs. Based on the raw logs shown in the exhibit, which statement is correct?
The correct answer is B. The action on firewall policy ID 1 is set to warning. The web filter logs indicate that traffic processed by firewall policy ID 1 triggered a warning action, allowing the user to proceed after acknowledging the warning.
Question
Refer to the web filter raw logs. Based on the raw logs shown in the exhibit, which statement is correct?
Exhibit
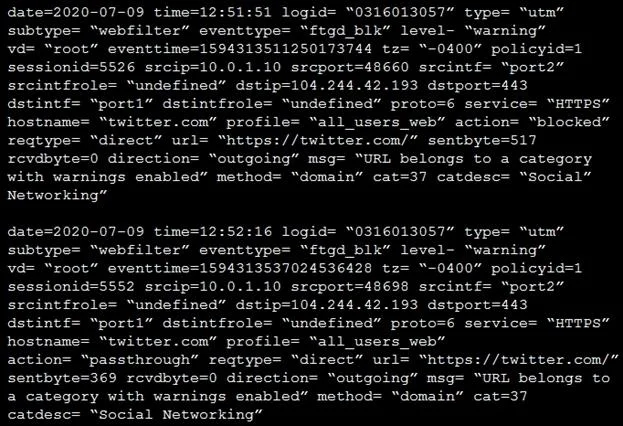
Options
- ASocial networking web filter category is configured with the action set to authenticate.
- BThe action on firewall policy ID 1 is set to warning.
- CAccess to the social networking web filter category was explicitly blocked to all users.
- DThe name of the firewall policy is all_users_web.
How the community answered
(19 responses)- A5% (1)
- B74% (14)
- C5% (1)
- D16% (3)
Why each option
The web filter logs indicate that traffic processed by firewall policy ID 1 triggered a warning action, allowing the user to proceed after acknowledging the warning.
If the action was "authenticate," the logs would display an authentication challenge or success/failure, not just a warning message, and users would need to provide credentials to proceed.
If the logs show an action like "warning" for a specific web filter category related to traffic handled by firewall policy ID 1, it means the firewall policy's web filter profile is configured with a warning action. A warning action allows users to access the content after clicking through a warning page, generating a log entry with the warning status, indicating the policy's configured behavior.
Concept tested: FortiGate web filter actions and log interpretation
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/469443/web-filter-profiles
Topics
Community Discussion
No community discussion yet for this question.