
NSE4_FGT-7.0 · Question #93
An administrator has configured the following settings: What does the configuration do? (Choose two.)
The correct answer is A. Reduces the amount of logs generated by denied traffic. D. Creates a session for traffic being denied. The configured settings create a temporary session for denied traffic by actively rejecting it and simultaneously reduce the amount of logs generated for this denied traffic.
Question
An administrator has configured the following settings:
What does the configuration do? (Choose two.)
Exhibit
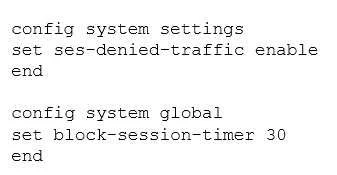
Options
- AReduces the amount of logs generated by denied traffic.
- BEnforces device detection on all interfaces for 30 minutes.
- CBlocks denied users for 30 minutes.
- DCreates a session for traffic being denied.
How the community answered
(35 responses)- A94% (33)
- B3% (1)
- C3% (1)
Why each option
The configured settings create a temporary session for denied traffic by actively rejecting it and simultaneously reduce the amount of logs generated for this denied traffic.
The configuration reduces the amount of logs by likely setting the firewall policy's logging option to disable or limit log generation for traffic that is explicitly denied, preventing excessive log entries from dropped packets.
There is no direct indication that the configuration enforces device detection or sets a 30-minute enforcement duration on all interfaces, as this is unrelated to denying traffic or logging.
The configuration is related to handling denied network traffic and its logging, not explicitly blocking specific *users* for a defined duration, which involves different authentication or security profile settings.
The configuration creates a session for traffic being denied, which is typically achieved by setting the firewall policy's action to actively 'reject' the traffic (e.g., by sending a TCP RST or ICMP unreachable message) instead of silently dropping it, necessitating a temporary session state for the response.
Concept tested: FortiGate firewall policy actions and logging
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/526786/firewall-policy
Topics
Community Discussion
No community discussion yet for this question.