
AZ-305 · Question #335
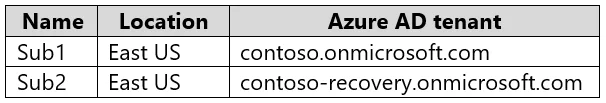
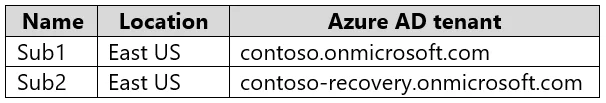
Hotspot Question You have the Azure subscriptions shown in the following table. Contoso.onmicrosft.com contains a user named User1. You need to deploy a solution to protect against ransomware…
The correct answer is Sub1:: A Recovery Services vault; Sub2:: A Resource Guard. To meet the requirements, a Recovery Services vault should be created in Sub1, and a Resource Guard should be created in Sub2. 1. Sub1: A Recovery Services vault The first requirement states: "Ensure that all the resources in Sub1 are backed up by using Azure Backup." An Azure…
Question
Exhibits
Answer Area
- Sub1:A Recovery Services vaultA Recovery Services vaultA Resource GuardAn Azure Site Recovery jobMicrosoft Azure Backup Server (MABS)The Microsoft Azure Recovery Services (MARS) agent
- Sub2:A Resource GuardA Recovery Services vaultA Resource GuardAn Azure Site Recovery jobMicrosoft Azure Backup Server (MABS)The Microsoft Azure Recovery Services (MARS) agent
Explanation
To meet the requirements, a Recovery Services vault should be created in Sub1, and a Resource Guard should be created in Sub2.
-
Sub1: A Recovery Services vault The first requirement states: "Ensure that all the resources in Sub1 are backed up by using Azure Backup." An Azure Recovery Services vault is the foundational Azure resource required to store backups for various Azure services, making it essential for implementing Azure Backup.
-
Sub2: A Resource Guard The second requirement specifies: "Require that User1 first be assigned a role for Sub2 before the user can make major changes to the backup configuration." This measure is intended to "protect against ransomware attacks." Azure Resource Guard is explicitly designed to enable multi-user authorization for critical operations on Azure Recovery Services vaults. By creating a Resource Guard in a separate subscription (Sub2 in this case) and linking it to the Recovery Services vault (presumably in Sub1), an additional layer of security is enforced. This ensures that sensitive backup operations (like disabling soft delete or deleting backups) require authorization from users assigned roles in the subscription containing the Resource Guard, thereby protecting against unauthorized or malicious changes to backup configurations, consistent with ransomware protection strategies. The link provided in the page's explanation (
https://learn.microsoft.com/en-us/azure/backup/multi-user-authorization) reinforces the use of Resource Guard for this purpose.
Topics
Community Discussion
No community discussion yet for this question.