
Microsoft
AZ-104 · Question #840
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might…
The correct answer is B. No. No correct answers at the moment. You create an inbound security rule that allows any traffic from the AzureLoadBalancer source and has a cost of 150. Cost settings does not affect blocked connections. You create an inbound security rule that denies all traffic from the…
Submitted by yuriko_h· Mar 4, 2026Configure and manage virtual networking
Question
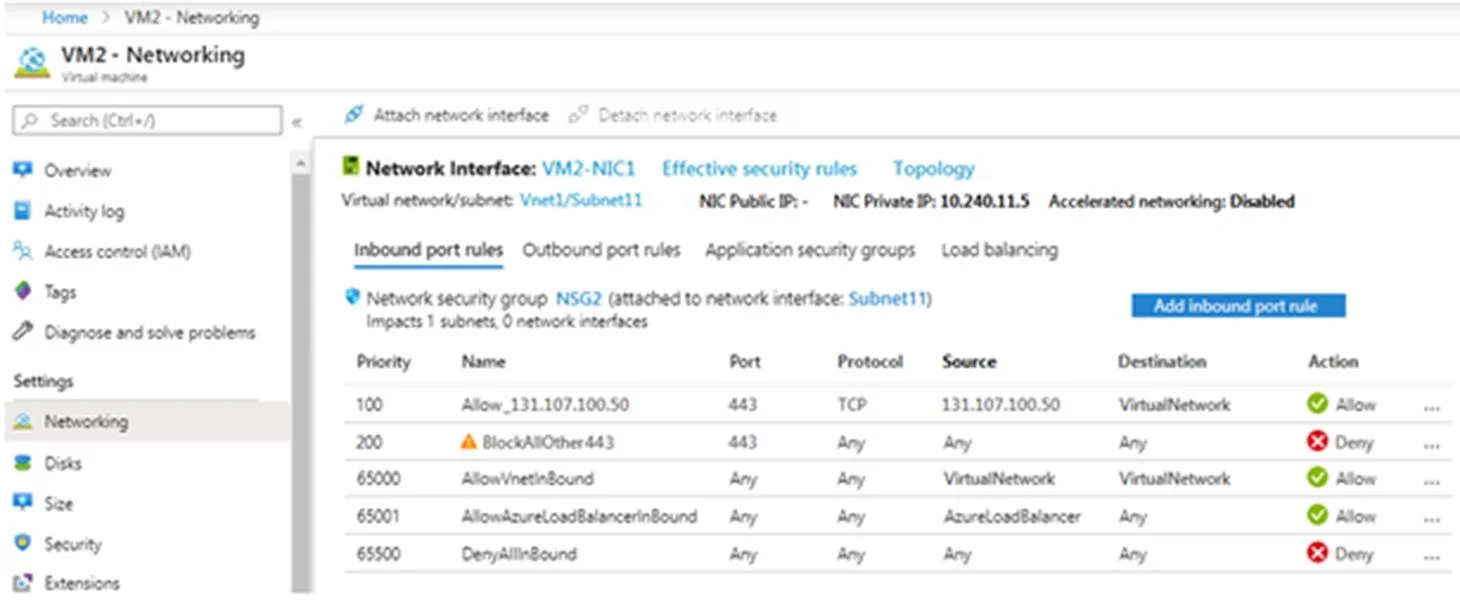
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution. After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen. You have an app named App1 that is installed on two Azure virtual machines named VM1 and VM2. Connections to App1 are managed by using an Azure Load Balancer. The effective network security configurations for VM2 are shown in the following exhibit. You discover that connections to App1 from 131.107.100.50 over TCP port 443 fail. You verify that the Load Balancer rules are configured correctly. You need to ensure that connections to App1 can be established successfully from 131.107.100.50 over TCP port 443. Solution: You create an inbound security rule that denies all traffic from the 131.107.100.50 source and has a priority 4096. Does this meet the goal?
Exhibits
Options
- AYes
- BNo
How the community answered
(41 responses)- A34% (14)
- B66% (27)
Explanation
- No correct answers at the moment. * You create an inbound security rule that allows any traffic from the AzureLoadBalancer source and has a cost of 150. Cost settings does not affect blocked connections. * You create an inbound security rule that denies all traffic from the 131.107.100.50 source and has a cost of 64999. Cost settings does not affect blocked connections. * You create an inbound security rule that denies all traffic from the 131.107.100.50 source and has a priority 4096. A deny rule does not allow more traffic. * You create an inbound security rule that denies all traffic from the 131.107.100.50 source and has a priority of 64999. A deny rule does not allow more traffic. * You delete the BlockAllOther443 inbound security rule. The Allow_131.107.100.50 rule is already overriding this block rule. * You modify the priority of the Allow_131.107.100.50 inbound security rule. This rule, with priority 100, already has the highest priority of all the rules. https://fastreroute.com/azure-network-security-groups-explained/
Community Discussion
No community discussion yet for this question.