
AZ-104 · Question #839
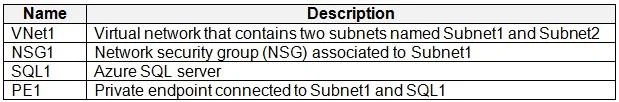
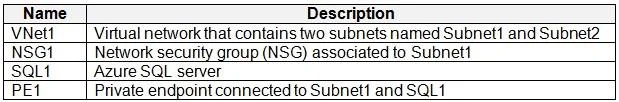
You have an Azure subscription that contains the resources shown in the following table. You need to add a rule to NSG1 that will restrict network access to PE1. What should you do first?
The correct answer is E. For Subnet1, configure a network policy for private endpoints. To restrict access to your Azure SQL Server via a Private Endpoint, the first crucial step is to enable Network Policy support for Network Security Groups (NSGs) on the subnet where the Private Endpoint resides; by default, this is disabled for Private Endpoints, so you must…
Question
Exhibits
Options
- AAssociate NSG1 to Subnet2.
- BCreate a subnet delegation for Microsoft.sql/managedInstances.
- CFor Subnet1, configure a service endpoint.
- DConfigure a user-defined route (UDR).
- EFor Subnet1, configure a network policy for private endpoints.
How the community answered
(32 responses)- A3% (1)
- B19% (6)
- C3% (1)
- D9% (3)
- E66% (21)
Explanation
To restrict access to your Azure SQL Server via a Private Endpoint, the first crucial step is to enable Network Policy support for Network Security Groups (NSGs) on the subnet where the Private Endpoint resides; by default, this is disabled for Private Endpoints, so you must explicitly enable it in the subnet's settings to allow NSG rules to filter traffic for the private endpoint. Here's a breakdown of the steps and why: *-> 1. Enable NSG Network Policies for the Subnet: Why: Azure Private Endpoints don't process NSG rules by default, even if the NSG is associated with the subnet. You must enable this specific subnet-level setting for the Private Endpoint to "see" the NSG rules. How: Go to your Virtual Network -> Subnets -> Select your subnet -> Configure "Network policies" for "Microsoft.Network/networkSecurityGroups" and set it to Enabled. 2. Create/Modify the NSG Rule 3. Disable Public Network Access on the SQL Server (Optional but Recommended): In summary, you must first enable the subnet's network policy for NSGs before your NSG rules will have any effect on the Private Endpoint's traffic, making it the critical first action. https://learn.microsoft.com/en-us/azure/azure-sql/database/vnet-service-endpoint-rule-overview
Community Discussion
No community discussion yet for this question.