
SY0-501 · Question #132
After a user reports stow computer performance, a systems administrator detects a suspicious file, which was installed as part of a freeware software package. The systems administrator reviews the…
The correct answer is A. RAT. RAT (Remote Access Trojan) - Option A A RAT (Remote Access Trojan) is the correct answer because it is commonly bundled with freeware software as a Trojan horse, silently installing itself to give an attacker remote control over the victim's system - which aligns with the slow…
Question
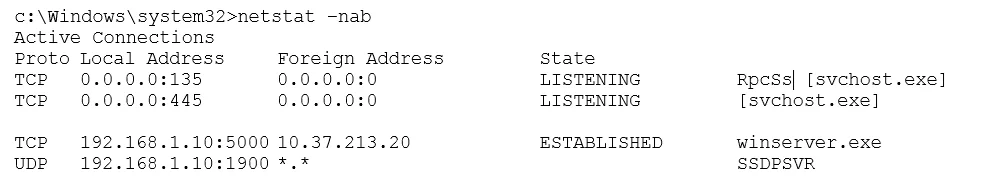
After a user reports stow computer performance, a systems administrator detects a suspicious file, which was installed as part of a freeware software package. The systems administrator reviews the output below:
Based on the above information, which of the following types of malware was installed on the user's computer?
Exhibit
Options
- ARAT
- BKeylogger
- CSpyware
- DWorm
- EBot
How the community answered
(24 responses)- A83% (20)
- B8% (2)
- D4% (1)
- E4% (1)
Explanation
RAT (Remote Access Trojan) - Option A
A RAT (Remote Access Trojan) is the correct answer because it is commonly bundled with freeware software as a Trojan horse, silently installing itself to give an attacker remote control over the victim's system - which aligns with the slow performance caused by unauthorized background processes. A Keylogger (B) specifically records keystrokes and wouldn't typically cause noticeable performance degradation on its own. Spyware (C) passively collects user data but is generally not installed with the same remote-control capabilities that a RAT provides. A Worm (D) self-replicates across networks without needing to be bundled with software, and a Bot (E) is typically deployed en masse as part of a botnet, rather than being disguised within a freeware package targeting an individual user.
Memory Tip: Think of a RAT like a rat hiding in a gift box - it sneaks in bundled with something that looks harmless (freeware), then quietly gnaws away at your system resources from the inside, giving the attacker a backdoor "remote" into your machine.
Topics
Community Discussion
No community discussion yet for this question.