
SC-300 · Question #94
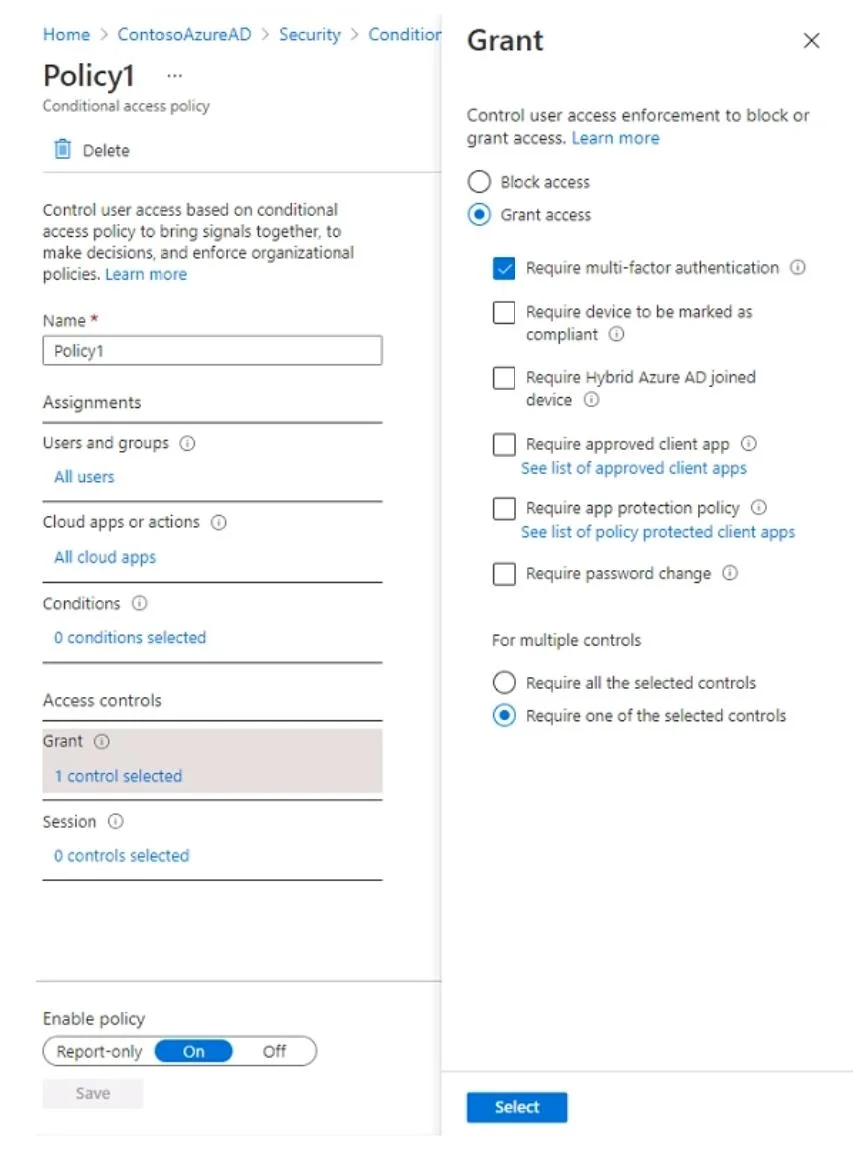
Hotspot Question You have a Microsoft 365 tenant. You configure a conditional access policy as shown in the Conditional Access policy exhibit. (Click the Conditional Access policy tab.) You view the…
The correct answer is Block access = No; Grant access = Yes; Require multi-factor authentication = Yes; Require device to be marked as compliant = No; Require Hybrid Azure AD joined device = No; Require approved client app = No; Require app protection policy = No; Require password change = No; Require all the selected controls = No; Require one of the selected controls = Yes. This question tests understanding of how Conditional Access policies interact with Privileged Identity Management (PIM) role settings and assignments in Microsoft 365, specifically around MFA requirements and activation conditions for privileged roles.
Question
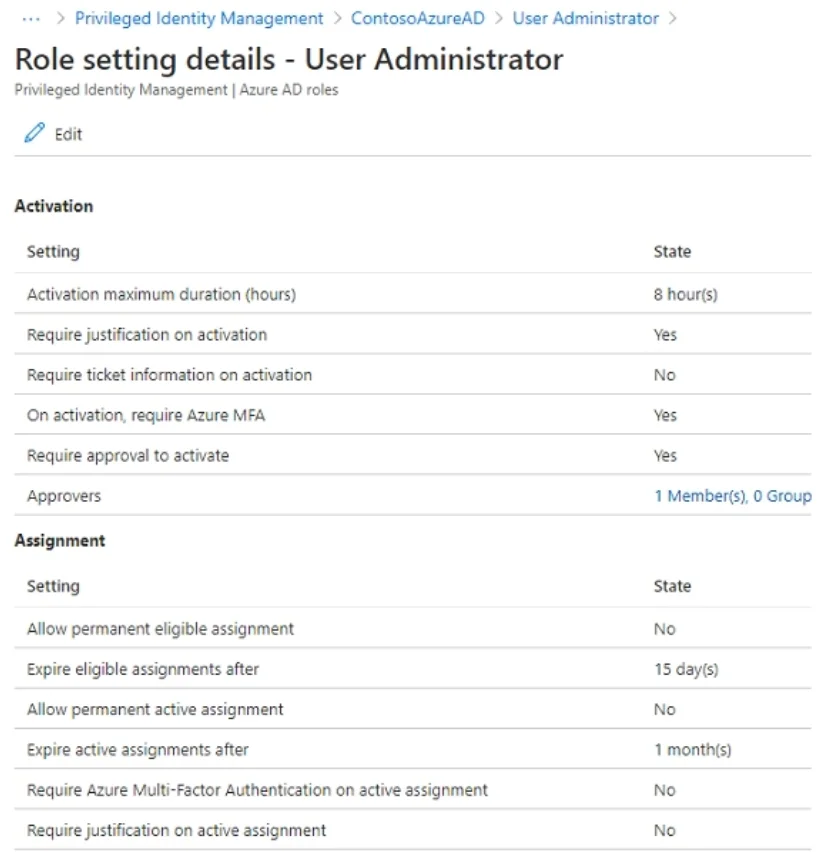
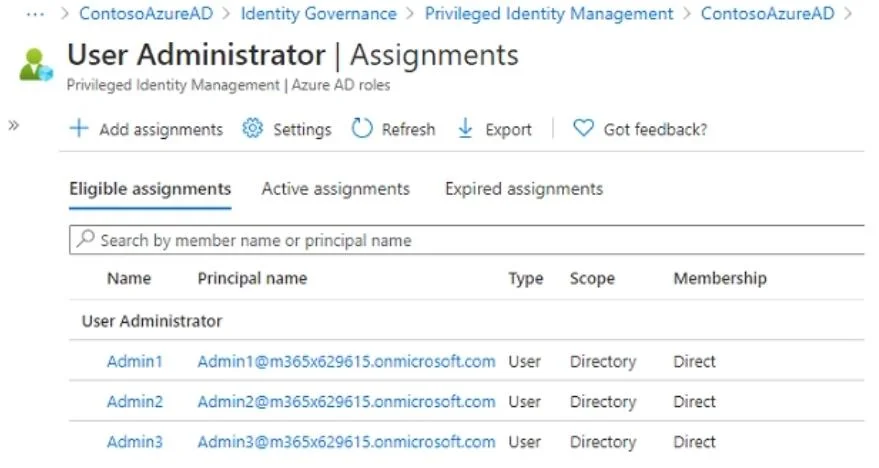
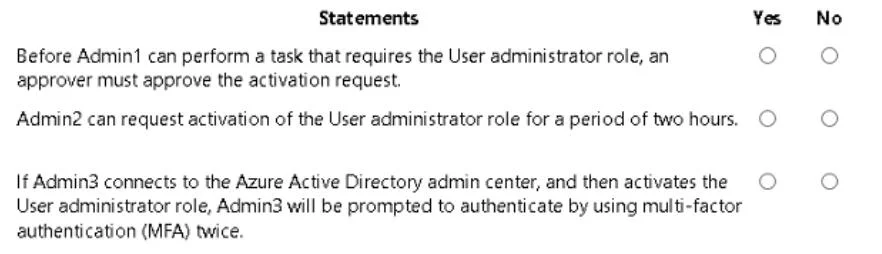
Hotspot Question You have a Microsoft 365 tenant. You configure a conditional access policy as shown in the Conditional Access policy exhibit. (Click the Conditional Access policy tab.) You view the User administrator role settings as shown in the Role setting details exhibit. (Click the Role setting details tab.) You view the User administrator role assignments as shown in the Role assignments exhibit. (Click the Role assignments tab.) For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point. Answer:
Exhibits
Answer Area
- Block accessNo
- Grant accessYes
- Require multi-factor authenticationYes
- Require device to be marked as compliantNo
- Require Hybrid Azure AD joined deviceNo
- Require approved client appNo
- Require app protection policyNo
- Require password changeNo
- Require all the selected controlsNo
- Require one of the selected controlsYes
Explanation
This question tests understanding of how Conditional Access policies interact with Privileged Identity Management (PIM) role settings and assignments in Microsoft 365, specifically around MFA requirements and activation conditions for privileged roles.
Approach. To answer each statement correctly, you must cross-reference three exhibits: (1) the Conditional Access policy which likely requires MFA for certain users or roles, (2) the Role setting details which define activation requirements (e.g., require MFA on activation, require justification, require approval), and (3) the Role assignments which show eligible vs. active assignments and which users are assigned. A user with an 'eligible' PIM assignment must activate the role and satisfy activation requirements (like MFA) defined in the Role settings. A Conditional Access policy targeting 'User administrator' or all users with MFA required would apply at sign-in or resource access time. If the Role setting requires MFA on activation AND the Conditional Access policy also requires MFA, the user must satisfy both. Users with 'active' (permanent) assignments bypass PIM activation but still must comply with Conditional Access. Always check whether the policy applies to the specific user type (guest vs. member), whether the assignment is eligible or active, and what activation controls are enforced in the Role settings detail.
Concept tested. Interaction between Microsoft Entra Conditional Access policies and Privileged Identity Management (PIM) role settings and assignments - including MFA enforcement at sign-in vs. role activation, eligible vs. active role assignments, and how activation requirements (MFA, justification, approval) in PIM Role settings complement or overlap with Conditional Access controls.
Reference. Microsoft Learn: Configure Azure AD role settings in Privileged Identity Management | Microsoft Learn: Conditional Access: Require MFA for Azure management - https://learn.microsoft.com/en-us/entra/id-governance/privileged-identity-management/pim-how-to-change-default-settings
Topics
Community Discussion
No community discussion yet for this question.