
NSE4_FGT-7.0 · Question #98
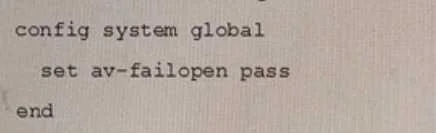
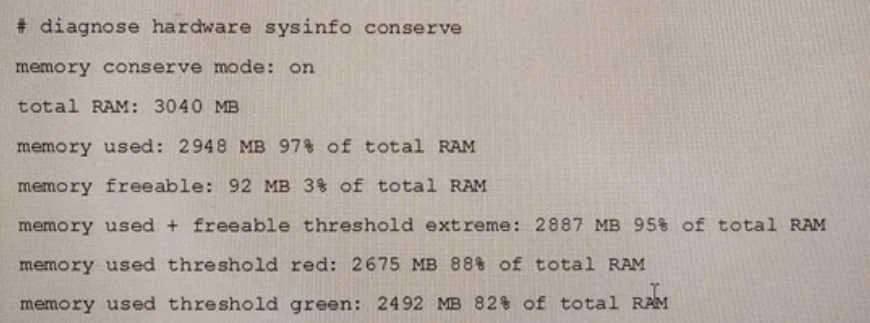
Examine this FortiGate configuration: Examine the output of the following debug command: Based on the diagnostic outputs above, how is the FortiGate handling the traffic for new sessions that…
The correct answer is C. It is dropped. Based on the provided correct answer, the FortiGate is configured to drop new network sessions that are identified as requiring inspection.
Question
Examine this FortiGate configuration:
Examine the output of the following debug command:
Based on the diagnostic outputs above, how is the FortiGate handling the traffic for new sessions that require inspection?
Exhibits
Options
- AIt is allowed, but with no inspection
- BIt is allowed and inspected as long as the inspection is flow based
- CIt is dropped.
- DIt is allowed and inspected, as long as the only inspection required is antivirus.
How the community answered
(47 responses)- A21% (10)
- B13% (6)
- C62% (29)
- D4% (2)
Why each option
Based on the provided correct answer, the FortiGate is configured to drop new network sessions that are identified as requiring inspection.
Allowing traffic without inspection would bypass the required inspection, which contradicts a dropping action based on inspection requirements.
If traffic is dropped, it is not allowed to proceed for inspection, regardless of whether that inspection is flow-based.
The correct answer indicates that the FortiGate is configured to drop new sessions requiring inspection. This behavior typically results from a security policy or inspection profile explicitly set to block such traffic, or due to a failure in the inspection process.
If traffic is dropped, it is not allowed for any type of inspection, including antivirus, as the session itself is terminated.
Concept tested: FortiGate traffic inspection and policy enforcement
Topics
Community Discussion
No community discussion yet for this question.