
NSE4_FGT-7.0 · Question #42
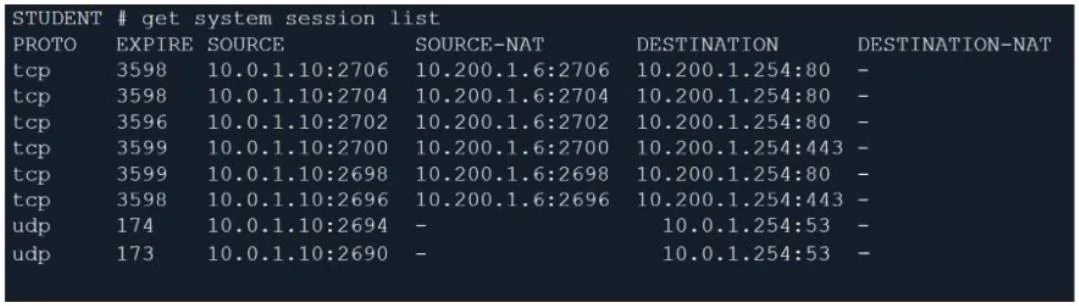
Refer to the exhibit. Which contains a session list output. Based on the information shown in the exhibit, which statement is true?
The correct answer is B. One-to-one NAT IP pool is used in the firewall policy. The exhibit, displaying a session list, indicates that a one-to-one NAT IP pool is actively used within the firewall policy, translating a private source IP to a dedicated public IP address.
Question
Refer to the exhibit. Which contains a session list output. Based on the information shown in the exhibit, which statement is true?
Exhibit
Options
- ADestination NAT is disabled in the firewall policy.
- BOne-to-one NAT IP pool is used in the firewall policy.
- COverload NAT IP pool is used in the firewall policy.
- DPort block allocation IP pool is used in the firewall policy.
How the community answered
(42 responses)- A5% (2)
- B81% (34)
- C12% (5)
- D2% (1)
Why each option
The exhibit, displaying a session list, indicates that a one-to-one NAT IP pool is actively used within the firewall policy, translating a private source IP to a dedicated public IP address.
Destination NAT is for incoming connections, translating the public destination IP to a private internal IP, and is unrelated to the source NAT configuration of outbound traffic.
One-to-one NAT maps each internal IP address to a unique external IP address from a defined IP pool without modifying source port numbers for outbound connections. The session list output would explicitly show a specific internal source IP being translated to a dedicated external IP from the pool, confirming this direct mapping.
Overload NAT (Port Address Translation - PAT) maps multiple internal IP addresses to a single external IP address, using different source port numbers for differentiation.
Port block allocation is a type of Overload NAT (PAT) where a range of source ports is reserved for specific internal hosts, still mapping multiple internal IPs to a limited set of external IPs or a single external IP.
Concept tested: Identifying NAT type from session list output
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/469493/ip-pool-based-nat
Topics
Community Discussion
No community discussion yet for this question.