
NSE4_FGT-7.0 · Question #68
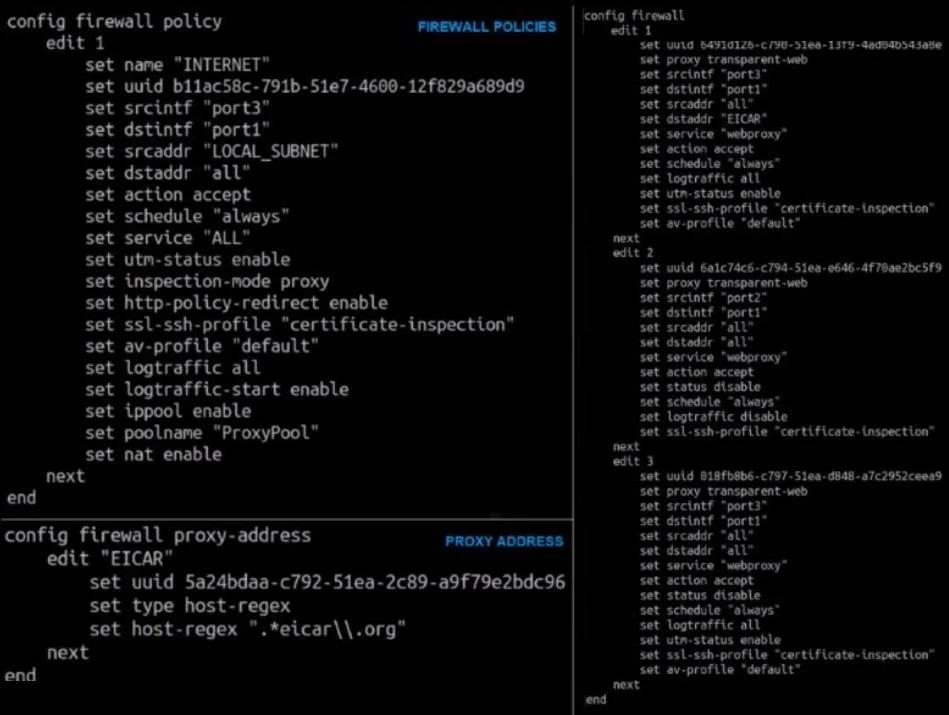
Refer to the exhibit. The exhibit shows a CLI output of firewall policies, proxy policies, and proxy addresses.
The correct answer is D. Traffic will be redirected to the transparent proxy and it will be denied by the proxy implicit deny. If traffic is configured to be redirected to a transparent proxy and no explicit proxy policy matches the traffic, it will be implicitly denied by the FortiGate proxy system.
Question
Refer to the exhibit. The exhibit shows a CLI output of firewall policies, proxy policies, and proxy addresses.
Exhibit
Options
- ATraffic will be redirected to the transparent proxy and it will be allowed by proxy policy ID 3.
- BTraffic will not be redirected to the transparent proxy and it will be allowed by firewall policy ID 1.
- CTraffic will be redirected to the transparent proxy and It will be allowed by proxy policy ID 1.
- DTraffic will be redirected to the transparent proxy and it will be denied by the proxy implicit deny
How the community answered
(31 responses)- A3% (1)
- B19% (6)
- C10% (3)
- D68% (21)
Why each option
If traffic is configured to be redirected to a transparent proxy and no explicit proxy policy matches the traffic, it will be implicitly denied by the FortiGate proxy system.
If proxy policy ID 3 were to allow the traffic, the traffic would be permitted, contradicting the fact that it is denied by the implicit deny rule, which only applies if no explicit policy matches.
When traffic is directed to a transparent proxy, it is processed by proxy policies. If the 'show proxy policy' output indicates that no explicit proxy policy (such as policy ID 1 or 3) matches the specific traffic characteristics, the traffic will fall through to the implicit deny rule at the end of the proxy policy list, thereby being denied.
Concept tested: FortiGate transparent proxy policy processing logic
Source: https://docs.fortinet.com/document/fortigate/7.4.0/handbook/356507/how-proxy-policies-work
Topics
Community Discussion
No community discussion yet for this question.