
NSE4_FGT-7.0 · Question #37
Examine this FortiGate configuration: Examine the output of the following debug command: Based on the diagnostic outputs above, how is the FortiGate handling the traffic for new sessions that…
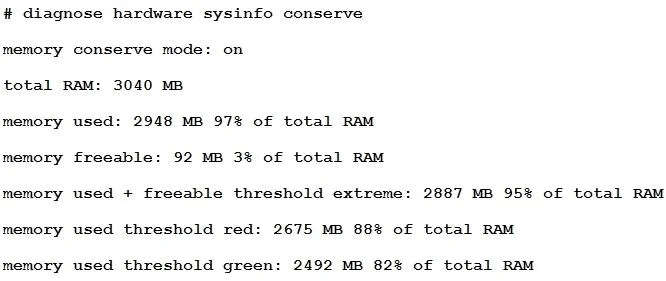
The correct answer is C. It is dropped. Based on the provided diagnostic output, new sessions requiring inspection are being dropped because the FortiGate is operating in conserve mode, which triggers a session drop for resource-intensive tasks.
Question
Examine this FortiGate configuration:
Examine the output of the following debug command:
Based on the diagnostic outputs above, how is the FortiGate handling the traffic for new sessions that require inspection?
Exhibit
Options
- AIt is allowed, but with no inspection
- BIt is allowed and inspected as long as the inspection is flow based
- CIt is dropped.
- DIt is allowed and inspected, as long as the only inspection required is antivirus.
How the community answered
(13 responses)- A8% (1)
- B8% (1)
- C62% (8)
- D23% (3)
Why each option
Based on the provided diagnostic output, new sessions requiring inspection are being dropped because the FortiGate is operating in conserve mode, which triggers a session drop for resource-intensive tasks.
If traffic were allowed, even without inspection, it wouldn't be dropped, which contradicts the behavior typically seen in conserve mode for new inspection-required sessions.
While flow-based inspection is generally less resource-intensive than proxy-based, FortiGate in conserve mode can still drop new sessions regardless of the inspection mode if the system resources are critically low. The primary action in conserve mode for new inspection sessions is to drop them.
The debug output would likely indicate that the FortiGate is in "conserve mode" due to high memory usage. When a FortiGate enters conserve mode, it prioritizes system stability by dropping new sessions that require resource-intensive processes like deep inspection (proxy-based inspection) to prevent memory exhaustion and potential crashes.
Antivirus inspection is a resource-intensive task. If only antivirus were required, traffic would still be dropped in conserve mode, as this is precisely the type of traffic FortiGate avoids processing to conserve resources.
Concept tested: FortiGate conserve mode behavior with new sessions requiring inspection
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/339178/conserve-mode
Topics
Community Discussion
No community discussion yet for this question.