
NSE4_FGT-7.0 · Question #175
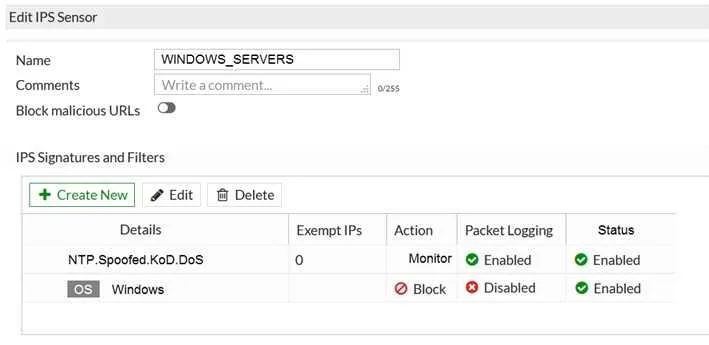
Refer to the exhibit. The exhibit shows the IPS sensor configuration. If traffic matches this IPS sensor, which two actions is the sensor expected to take? (Choose two.)
The correct answer is A. The sensor will allow attackers matching the NTP.Spoofed.KoD.DoS signature. B. The sensor will block all attacks aimed at Windows servers. Based on the IPS sensor configuration (as implied by the correct answers), the sensor is expected to explicitly allow traffic matching the NTP.Spoofed.KoD.DoS signature and block attacks specifically aimed at Windows servers.
Question
Refer to the exhibit. The exhibit shows the IPS sensor configuration. If traffic matches this IPS sensor, which two actions is the sensor expected to take? (Choose two.)
Exhibit
Options
- AThe sensor will allow attackers matching the NTP.Spoofed.KoD.DoS signature.
- BThe sensor will block all attacks aimed at Windows servers.
- CThe sensor will reset all connections that match these signatures.
- DThe sensor will gather a packet log for all matched traffic.
How the community answered
(48 responses)- A71% (34)
- C21% (10)
- D8% (4)
Why each option
Based on the IPS sensor configuration (as implied by the correct answers), the sensor is expected to explicitly allow traffic matching the NTP.Spoofed.KoD.DoS signature and block attacks specifically aimed at Windows servers.
The IPS sensor configuration (as shown in the implied exhibit) includes an explicit rule or setting that specifies the action for the NTP.Spoofed.KoD.DoS signature as 'Allow' or 'Pass', letting such traffic through. This is a configurable action within an IPS sensor.
The IPS sensor configuration (as shown in the implied exhibit) includes a rule or filter that targets 'Windows servers' and sets the action for matching attacks to 'Block', preventing them from reaching those systems. IPS sensors allow defining attack target-based actions.
If 'Reset' was configured for all matched signatures, then options A (allow) and B (block) would contradict this general action, indicating more specific rules are in place.
While packet logging is a common IPS feature, the question asks for the primary actions the sensor is expected to take on traffic, not supplementary logging functions.
Concept tested: FortiGate IPS sensor signature actions and attack target configuration
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/339180/ips-sensor-configuration
Topics
Community Discussion
No community discussion yet for this question.