
NSE4_FGT-7.0 · Question #140
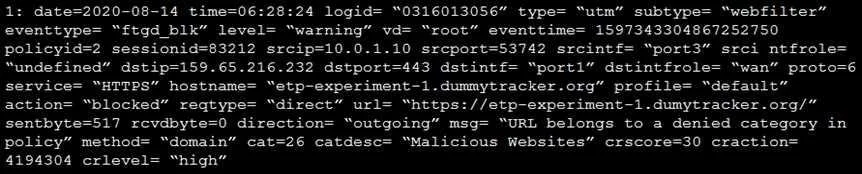
Refer to the exhibit. Based on the raw log, which two statements are correct? (Choose two.)
The correct answer is A. Traffic is blocked because Action is set to DENY in the firewall policy. C. This is a security log. The raw log indicates that traffic was explicitly denied by a firewall policy and that such a denial constitutes a security-relevant event within FortiGate logging.
Question
Refer to the exhibit. Based on the raw log, which two statements are correct? (Choose two.)
Exhibit
Options
- ATraffic is blocked because Action is set to DENY in the firewall policy.
- BTraffic belongs to the root VDOM.
- CThis is a security log.
- DLog severity is set to error on FortiGate.
How the community answered
(47 responses)- A72% (34)
- B9% (4)
- D19% (9)
Why each option
The raw log indicates that traffic was explicitly denied by a firewall policy and that such a denial constitutes a security-relevant event within FortiGate logging.
If the log shows 'action=deny', it directly signifies that the firewall policy was configured to block the traffic as its specified action.
Without the raw log explicitly stating 'vdom=root', there is no technical basis to conclude that the traffic belongs to the root VDOM, as traffic can originate from any configured VDOM.
Logs indicating traffic denial by a firewall policy are considered security-related events, often categorized under security logs or security event types in FortiGate's logging and reporting.
An 'action=deny' in a traffic log is typically classified with an informational or notification severity level, not usually as an 'error' severity, which is reserved for system malfunctions or more critical issues.
Concept tested: FortiGate log analysis (Action, Log Type)
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/526715/log-settings
Topics
Community Discussion
No community discussion yet for this question.