
NSE4 · Question #319
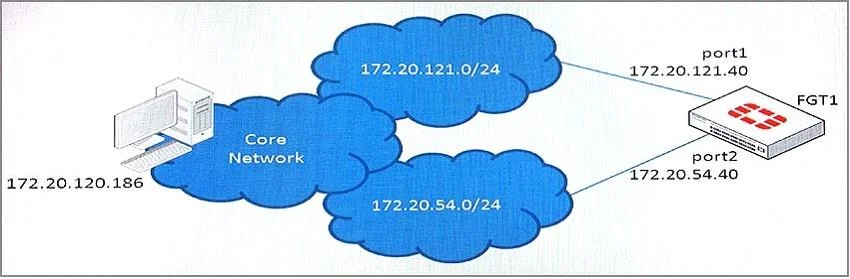
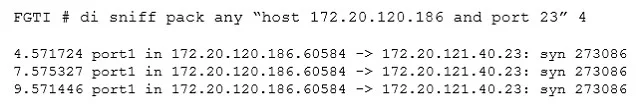
View the exhibit. This is a sniffer output of a telnet connection request from 172.20.120.186 to the port1 interface of FGT1. In this scenario. FGT1 has the following routing table: Assuming telnet…
The correct answer is B. The connection is dropped due to reverse path forwarding check. The FortiGate is not responding to the telnet request likely due to a Reverse Path Forwarding (RPF) check failure, as the sniffer shows the incoming traffic but the routing table indicates no path back to the source.
Question
View the exhibit. This is a sniffer output of a telnet connection request from 172.20.120.186 to the port1 interface of FGT1. In this scenario. FGT1 has the following routing table:
Assuming telnet service is enabled for port1, which of the following statements correctly describes why FGT1 is not responding?
Exhibits
Options
- AThe port1 cable is disconnected.
- BThe connection is dropped due to reverse path forwarding check.
- CThe connection is denied due to forward policy check.
- DFGT1's port1 interface is administratively down.
How the community answered
(59 responses)- A3% (2)
- B76% (45)
- C7% (4)
- D14% (8)
Why each option
The FortiGate is not responding to the telnet request likely due to a Reverse Path Forwarding (RPF) check failure, as the sniffer shows the incoming traffic but the routing table indicates no path back to the source.
If the port1 cable were disconnected, the sniffer would not show incoming packets on port1.
A Reverse Path Forwarding (RPF) check verifies that the FortiGate has a valid route back to the source IP address of an incoming packet; if no such route exists for 172.20.120.186, the packet is dropped.
A forward policy check determines if a firewall policy denies the connection, but an RPF check occurs earlier in the packet flow, dropping traffic before policy evaluation if the return path is invalid.
If port1 were administratively down, it would not be able to receive traffic, contradicting the sniffer output showing incoming packets.
Concept tested: FortiGate RPF check
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/33948/packet-flow-overview
Topics
Community Discussion
No community discussion yet for this question.