
NSE4 · Question #223
Review the IPsec phase1 configuration in the Exhibit shown below; then answer the question following it. Which of the following statements are correct regarding this configuration? (Select all that…
The correct answer is A. The phase1 is for a route-based VPN configuration. C. The local gateway IP is the address assigned to port1. The IPsec phase1 configuration creates a dedicated tunnel interface (phase1-interface), defining a route-based VPN where the local gateway IP is explicitly tied to the port1 interface.
Question
Review the IPsec phase1 configuration in the Exhibit shown below; then answer the question following it. Which of the following statements are correct regarding this configuration? (Select all that apply).
Exhibit
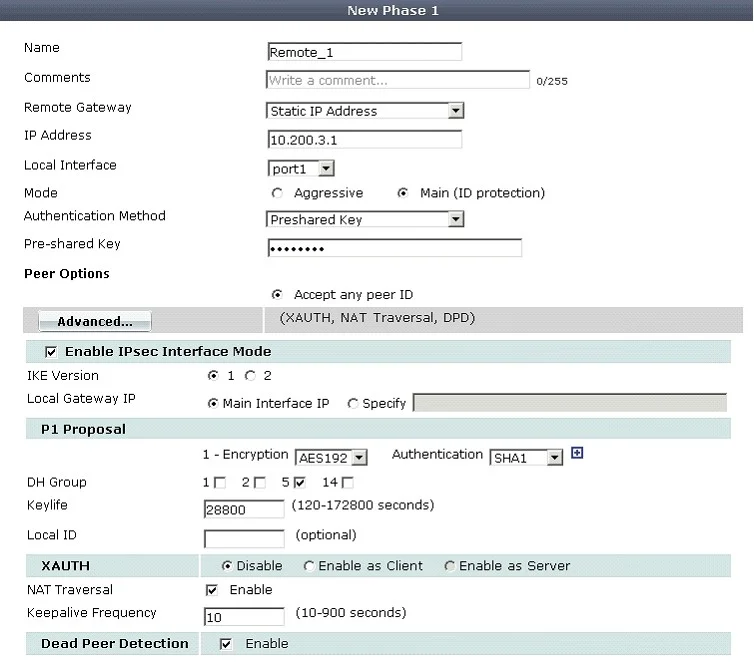
Options
- AThe phase1 is for a route-based VPN configuration.
- BThe phase1 is for a policy-based VPN configuration.
- CThe local gateway IP is the address assigned to port1.
- DThe local gateway IP address is 10.200.3.1.
How the community answered
(27 responses)- A74% (20)
- B19% (5)
- D7% (2)
Why each option
The IPsec phase1 configuration creates a dedicated tunnel interface (`phase1-interface`), defining a route-based VPN where the local gateway IP is explicitly tied to the `port1` interface.
The command `config vpn ipsec phase1-interface` is used to create a tunnel interface, which is the defining characteristic of a route-based IPsec VPN. In route-based VPNs, traffic is directed into the tunnel using routing table entries rather than firewall policies.
Policy-based VPNs are configured using `config vpn ipsec phase1` (without `-interface`) and rely on firewall policies to match traffic and direct it through the VPN, rather than a dedicated tunnel interface.
The configuration includes `set interface port1` and `set local-gw 10.100.1.1`. This explicitly binds the local gateway IP of 10.100.1.1 to the physical `port1` interface, meaning that 10.100.1.1 must be the IP address assigned to `port1` for the VPN to establish correctly.
The `set local-gw 10.100.1.1` command explicitly sets the local gateway IP address to 10.100.1.1, while 10.200.3.1 is configured as the `remote-gw`.
Concept tested: IPsec VPN types (route-based vs. policy-based)
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/155982/ipsec-vpn-types-route-based-and-policy-based
Topics
Community Discussion
No community discussion yet for this question.