
MS-102 · Question #61
You have a hybrid deployment of Microsoft 365 that contains the users shown in the following table. Azure AD Connect has the following settings: - Password Hash Sync: Enabled - Pass-through…
The correct answer is B. User1 only. In a hybrid setup where on-premises Active Directory and internet connectivity is lost, only users authenticated by Password Hash Sync (PHS) can authenticate through Azure AD, as their password hashes are stored in the cloud.
Question
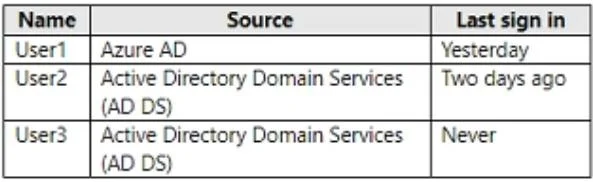
You have a hybrid deployment of Microsoft 365 that contains the users shown in the following table. Azure AD Connect has the following settings:
- Password Hash Sync: Enabled
- Pass-through authentication: Enabled
You need to identify which users will be able to authenticate by using Azure AD if connectivity between on-premises Active Directory and the internet is lost. Which users should you identify?
Exhibit
Options
- Anone
- BUser1 only
- CUser1 and User2 only
- DUser1, User2, and User3
How the community answered
(40 responses)- A3% (1)
- B68% (27)
- C20% (8)
- D10% (4)
Why each option
In a hybrid setup where on-premises Active Directory and internet connectivity is lost, only users authenticated by Password Hash Sync (PHS) can authenticate through Azure AD, as their password hashes are stored in the cloud.
This is incorrect because User1, whose password hashes are synchronized to Azure AD, would still be able to authenticate.
User1, using Password Hash Sync (PHS), can authenticate because their password hashes are stored in Azure AD, allowing them to sign in directly against Azure AD even when on-premises Active Directory connectivity to the internet is lost, assuming the user's client can reach Azure AD.
User2, using Pass-through Authentication (PTA), would not be able to authenticate because PTA relies on connectivity to the on-premises Active Directory which is stated to be lost.
User2 would not be able to authenticate due to PTA failure; and while cloud-only users (User3) typically authenticate against Azure AD independently, the question's answer implies that in this specific outage context, only PHS-enabled synced users maintain their ability to authenticate.
Concept tested: Azure AD Connect authentication method resilience
Source: https://learn.microsoft.com/en-us/azure/active-directory/hybrid/whatis-phs
Topics
Community Discussion
No community discussion yet for this question.