
350-501 · Question #392
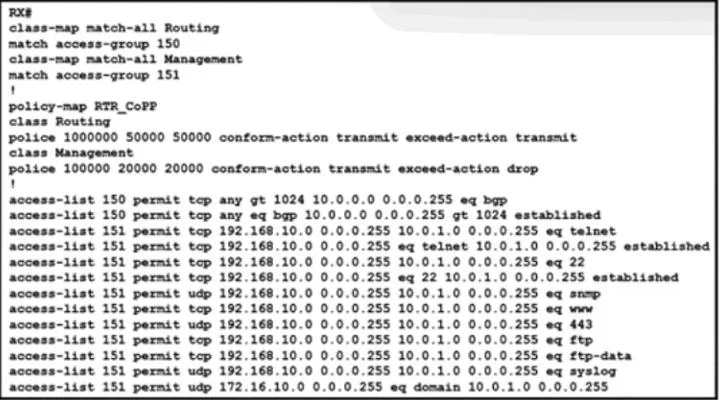
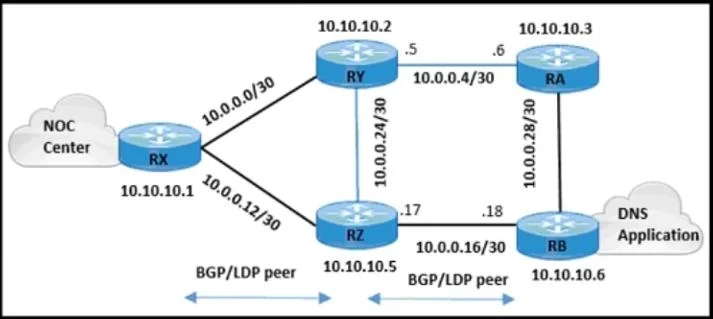
Refer to the exhibit. The engineering team wants to limit control traffic on router RX with the following IP address assignments: - Accepted traffic for router: 10.0.0.0/24 - NOC users IP…
The correct answer is B. RX(config)#access-list 150 permit tcp any gt 1024 10.0.0.0 0.0.0.255 eq 639. To limit MSDP control traffic to a specific router subnet (10.0.0.0/24) with standard client ephemeral source ports, an extended access list must permit TCP traffic from any source with high-numbered source ports to the destination network on MSDP's well-known TCP port 639.
Question
Refer to the exhibit. The engineering team wants to limit control traffic on router RX with the following IP address assignments:
- Accepted traffic for router: 10.0.0.0/24
- NOC users IP allocation: 192.168.10.0/24
Which additional configuration must be applied to RX to apply the policy for MSDP?
Exhibits
Options
- ARX(config)#access-list 151 permit tcp any gt 1024 10.10.0.0 0.0.0.255 eq 639
- BRX(config)#access-list 150 permit tcp any gt 1024 10.0.0.0 0.0.0.255 eq 639
- CRX(config)#access-list 151 permit tcp any 10.0.0.0 0.0.0.255 eq 639
- DRX(config)#access-list 150 permit tcp any 10.0.0.0 0.0.0.255 eq 639
How the community answered
(30 responses)- A17% (5)
- B73% (22)
- C3% (1)
- D7% (2)
Why each option
To limit MSDP control traffic to a specific router subnet (10.0.0.0/24) with standard client ephemeral source ports, an extended access list must permit TCP traffic from any source with high-numbered source ports to the destination network on MSDP's well-known TCP port 639.
This option is incorrect because it specifies the destination network as `10.10.0.0/24`, which does not match the required `10.0.0.0/24` subnet for accepted router traffic.
This command creates an extended access list (150) that permits TCP traffic from any source IP using source ports greater than 1024, destined for the 10.0.0.0/24 network, on TCP port 639, which is the well-known port for MSDP, precisely matching the requirements for limiting MSDP control traffic.
This option is incorrect because it omits the `gt 1024` keyword for the source port, which is commonly used to specify client ephemeral ports and is implied for precise control traffic limiting.
This option is incorrect because it omits the `gt 1024` keyword for the source port, which is commonly used to specify client ephemeral ports and is implied for precise control traffic limiting.
Concept tested: Extended ACL configuration for control plane traffic
Source: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_data_acl/configuration/xe-16/sec-data-acl-xe-16-book/sec-extended-ip-acls.html
Topics
Community Discussion
No community discussion yet for this question.