
SY0-501 · Question #330
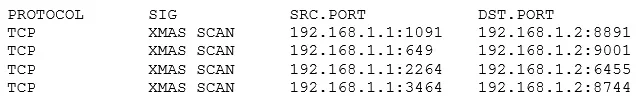
A security analyst has received the following alert snippet from the HIDS appliance: Given the above logs, which of the following is the cause of the attack?
The correct answer is B. FIN, URG, and PSH flags are set in the packet header. The attack described is a port scan technique detected by the HIDS appliance due to an unusual combination of TCP flags in the packet header.
Question
A security analyst has received the following alert snippet from the HIDS appliance:
Given the above logs, which of the following is the cause of the attack?
Exhibit
Options
- AThe TCP ports on destination are all open
- BFIN, URG, and PSH flags are set in the packet header
- CTCP MSS is configured improperly
- DThere is improper Layer 2 segmentation
How the community answered
(52 responses)- A6% (3)
- B81% (42)
- C2% (1)
- D12% (6)
Why each option
The attack described is a port scan technique detected by the HIDS appliance due to an unusual combination of TCP flags in the packet header.
The TCP ports being open on the destination is a condition an attacker might exploit or discover, not the cause or method of the attack itself.
Setting FIN, URG, and PSH flags simultaneously in a TCP packet header is characteristic of certain covert port scanning techniques, such as an Xmas scan (which typically includes RST) or specific Nmap scans. This non-standard flag combination is an anomaly that a Host Intrusion Detection System (HIDS) would flag as malicious probing activity, aiming to elicit responses from open ports while potentially bypassing firewalls.
Improper TCP MSS configuration is related to network performance and maximum segment size, and is not a direct 'cause of an attack' in the context of a HIDS alert for packet anomalies.
Improper Layer 2 segmentation describes a network vulnerability that could allow an attack to occur, but it is not the specific technique or cause of the attack identified by packet flags.
Concept tested: TCP flag-based port scanning techniques
Source: https://learn.microsoft.com/en-us/windows/security/threat-protection/auditing/event-4624
Topics
Community Discussion
No community discussion yet for this question.