
SY0-501 · Question #184
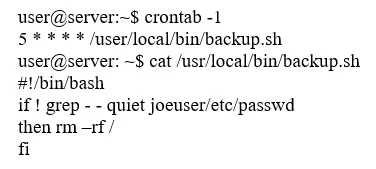
An information security specialist is reviewing the following output from a Linux server. Based on the above information, which of the following types of malware was installed on the server?
The correct answer is A. Logic bomb. The analysis of the Linux server output indicated a type of malware designed to execute malicious code only upon meeting specific, predefined conditions, which is the hallmark of a logic bomb.
Question
An information security specialist is reviewing the following output from a Linux server. Based on the above information, which of the following types of malware was installed on the server?
Exhibit
Options
- ALogic bomb
- BTrojan
- CBackdoor
- DRansomware
- ERootkit
How the community answered
(23 responses)- A78% (18)
- B4% (1)
- C13% (3)
- D4% (1)
Why each option
The analysis of the Linux server output indicated a type of malware designed to execute malicious code only upon meeting specific, predefined conditions, which is the hallmark of a logic bomb.
A logic bomb is a malicious program or code snippet that lies dormant within a system until a predefined event or condition triggers its execution. This condition could be a specific date and time, the launch of a particular program, a user action, or a change in system state, making it difficult to detect before activation.
A Trojan disguises itself as legitimate software to trick users into installing it, focusing on deceptive delivery rather than solely conditional execution.
A backdoor provides unauthorized remote access to a system, typically bypassing normal authentication or encryption, rather than waiting for a specific trigger condition.
Ransomware encrypts a victim's files and demands a ransom for their release, which would manifest as encrypted data and ransom notes, not necessarily a dormant conditional trigger.
A rootkit is designed to hide its presence and the presence of other malicious software from detection, often by modifying operating system components, rather than being defined by a conditional activation.
Concept tested: Malware identification (Logic Bomb)
Source: https://www.microsoft.com/en-us/security/business/security-101/what-is-a-logic-bomb
Topics
Community Discussion
No community discussion yet for this question.