
SPLK-1003 · Question #48
In this source definition the MAX_TIMESTAMP_LOOKHEAD is missing. Which value would fit best? Event example:
The correct answer is D. MAX TIMESTAMP LOOKAHEAD -30. https://docs.splunk.com/Documentation/Splunk/6.2.0/Data/Configuretimestamprecognition Specify how far (how many characters) into an event Splunk software should look for a timestamp." since TIME_PREFIX = ^ and timestamp is from 0-29 position, so D=30 will pick up the WHOLE…
Question
In this source definition the MAX_TIMESTAMP_LOOKHEAD is missing. Which value would fit best? Event example:
Exhibit
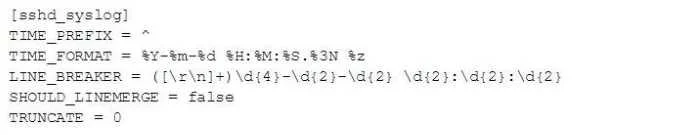
Options
- AMAX_TIMESTAMP_L0CKAHEAD = 5
- BMAX_TIMESTAMP_LOOKAHEAD -10
- CMAX_TIMESTAMF_LOOKHEAD = 20
- DMAX TIMESTAMP LOOKAHEAD -30
How the community answered
(24 responses)- A4% (1)
- C4% (1)
- D92% (22)
Explanation
https://docs.splunk.com/Documentation/Splunk/6.2.0/Data/Configuretimestamprecognition Specify how far (how many characters) into an event Splunk software should look for a timestamp." since TIME_PREFIX = ^ and timestamp is from 0-29 position, so D=30 will pick up the WHOLE timestamp correctly.
Topics
Community Discussion
No community discussion yet for this question.