
SC-300 · Question #71
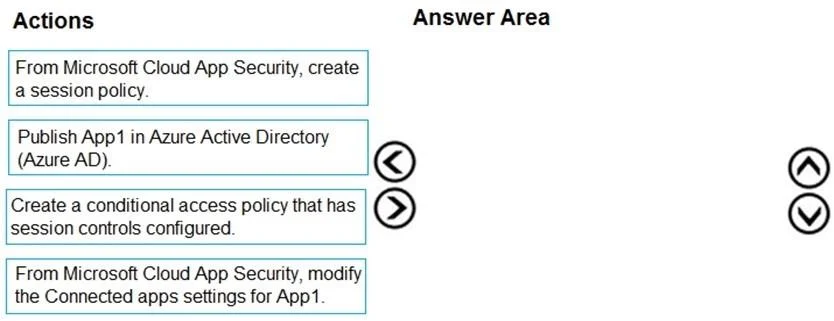
Drag and Drop Question You have a Microsoft 365 E5 tenant. You purchase a cloud app named App1. You need to enable real-time session-level monitoring of App1 by using Microsoft Cloud App Security…
The correct answer is Publish App1 in Azure Active Directory (Azure AD).; Create a conditional access policy that has session controls configured.; From Microsoft Cloud App Security, modify the Connected apps settings for App1.; From Microsoft Cloud App Security, create a session policy. The correct order follows the logical dependency chain for enabling Conditional Access App Control in Microsoft Cloud App Security (MCAS). First, App1 must be published in Azure AD so it can be recognized as a managed application. Next, a Conditional Access policy with session…
Question
Exhibit
Answer Area
Drag items
Correct arrangement
- Publish App1 in Azure Active Directory (Azure AD).
- Create a conditional access policy that has session controls configured.
- From Microsoft Cloud App Security, modify the Connected apps settings for App1.
- From Microsoft Cloud App Security, create a session policy.
Explanation
The correct order follows the logical dependency chain for enabling Conditional Access App Control in Microsoft Cloud App Security (MCAS). First, App1 must be published in Azure AD so it can be recognized as a managed application. Next, a Conditional Access policy with session controls is created to route traffic through MCAS as a reverse proxy. Then, MCAS must be configured to recognize and onboard App1 via the Connected Apps settings, and finally a session policy is created within MCAS to define the specific real-time monitoring or control actions to apply. Each step depends on the previous one being completed first.
Topics
Community Discussion
No community discussion yet for this question.