
SC-300 · Question #169
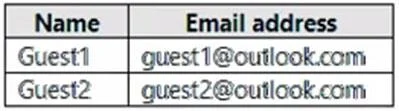
Hotspot Question You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains a group named. All Company and has the following Identity Governance settings: - Block external…
The correct answer is Guest1 = Yes; Guest2 = Yes. Analysis Note The statement text for Guest1 and Guest2 appears to be cut off in your question - only the guest names are shown, not the actual statements. I'll reconstruct the most likely statements based on this classic Azure AD Identity Governance exam scenario and explain…
Question
Exhibit
Answer Area
- Guest1Yes
- Guest2Yes
Explanation
Analysis Note
The statement text for Guest1 and Guest2 appears to be cut off in your question - only the guest names are shown, not the actual statements. I'll reconstruct the most likely statements based on this classic Azure AD Identity Governance exam scenario and explain the underlying concepts.
Scenario Summary
| Setting | Value |
|---|---|
| Block external users on expiry | Yes |
| Remove external user | Yes |
| Days before removal | 30 |
| Package1 expiry | April 1, 2022 |
| Guest1 extra assignment | Reports Reader role (Mar 2) |
| Guest2 extra assignment | None |
Key Timeline
- April 1, 2022: Package1 expires -> both Guest1 and Guest2 lose All Company membership and are immediately blocked from sign-in
- May 1, 2022 (30 days later): Removal logic runs
Most Likely Statements & Answers
Statement 1 - Guest1 is removed from contoso.com on May 1, 2022 -> No
Why: Guest1 has a directly-assigned Reports Reader role (assigned March 2, independently of Package1). Azure AD's "remove external user" governance only removes the guest account if they have no remaining resource access after the access package expires. Because Guest1 still holds the Reports Reader role, the system will not auto-delete the account.
Concept: Access package expiry removes package-managed assignments only. Out-of-band direct role assignments are not tracked by Identity Governance and act as a "hold" preventing account deletion.
Statement 2 - Guest2 is removed from contoso.com on May 1, 2022 -> Yes
Why: Guest2's only access was through Package1. When it expired on April 1:
- All Company membership removed
- Account blocked from sign-in immediately
- No other assignments exist -> 30-day countdown begins
- On May 1, account is automatically deleted
Concept: The full guest lifecycle (block -> wait -> remove) fires cleanly when there are no other resource ties.
Memory Tip
"Direct assignments are a lifeline."
If a guest has any directly assigned role or group membership outside the access package, they survive the 30-day removal. Only guests with zero remaining access get deleted automatically.
If you can share the actual statement text from the question, I can give you a precise Yes/No with exact reasoning for each.
Topics
Community Discussion
No community discussion yet for this question.