
SC-300 · Question #148
Hotspot Question You have a Microsoft 365 tenant that has 5,000 users. One hundred of the users are executives. The executives have a dedicated support team. You need to ensure that the support team…
This question tests whether you can correctly scope an Azure AD administrative role to a specific subset of users (executives) using the principle of least privilege, rather than granting tenant-wide administrative rights.
Question
Hotspot Question You have a Microsoft 365 tenant that has 5,000 users. One hundred of the users are executives. The executives have a dedicated support team. You need to ensure that the support team can reset passwords and manage multi-factor authentication (MFA) settings for only the executives. The solution must use the principle of least privilege. Which object type and Azure Active Directory (Azure AD) role should you use? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point. Answer:
Exhibit
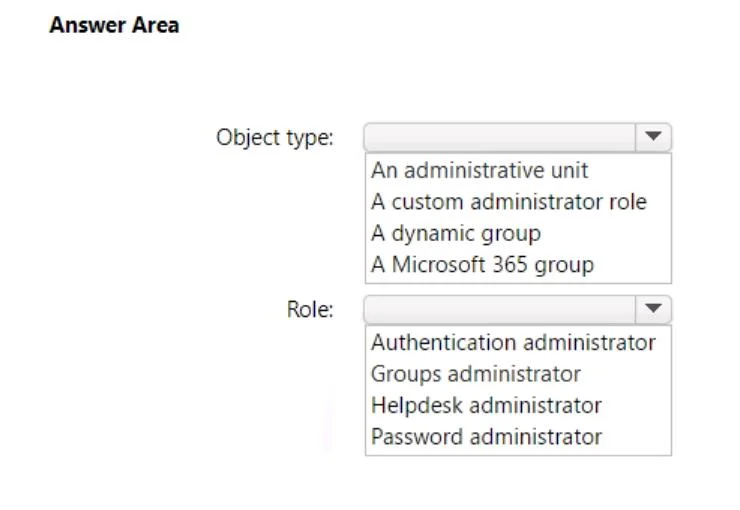
Answer Area
- Object type:An administrative unitA custom administrator roleA dynamic groupA Microsoft 365 group
- Role:Authentication administratorGroups administratorHelpdesk administratorPassword administrator
Explanation
This question tests whether you can correctly scope an Azure AD administrative role to a specific subset of users (executives) using the principle of least privilege, rather than granting tenant-wide administrative rights.
Approach. The correct object type is an Administrative Unit (AU). You should place the 100 executive accounts into a dedicated Administrative Unit. The correct Azure AD role is Authentication Administrator (scoped to that Administrative Unit). An Administrative Unit allows you to restrict the scope of a role assignment so it only applies to members within that AU - meaning the support team can reset passwords and manage MFA settings exclusively for the executives, not all 5,000 users. The Authentication Administrator role specifically grants permission to reset passwords and manage MFA/authentication methods for non-admin users, satisfying least privilege. If the executives were themselves admins, you would need the Privileged Authentication Administrator role instead.
Concept tested. Azure AD Administrative Units (scoped role assignments) and the principle of least privilege - specifically using Administrative Units to restrict the blast radius of a delegated admin role (Authentication Administrator) to a defined subset of users rather than granting tenant-wide permissions.
Reference. https://learn.microsoft.com/en-us/azure/active-directory/roles/administrative-units
Topics
Community Discussion
No community discussion yet for this question.