
SC-300 · Question #147
Drag and Drop Question You have a Microsoft 365 E5 subscription that contains two users named User1 and User2. You need to ensure that User1 can create access reviews for groups, and that User2 can…
The correct answer is User administrator; Security reader. User Administrator is the least-privileged role that grants the ability to create access reviews for groups, as it includes permissions to manage group memberships and identity governance tasks without full admin rights. Security Reader is the least-privileged role that allows…
Question
Exhibit
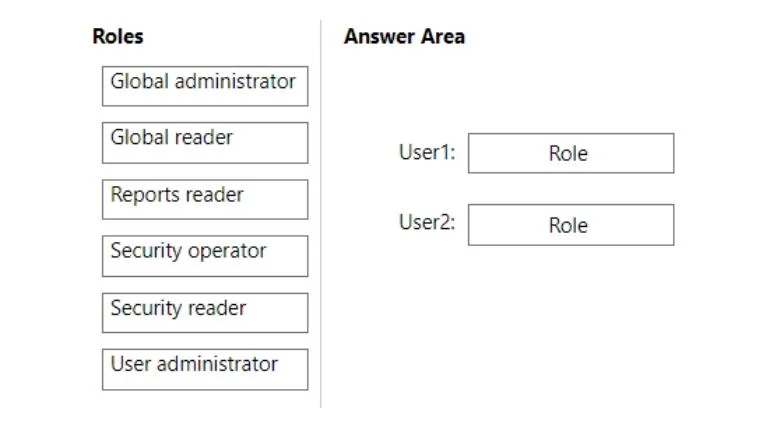
Answer Area
Drag items
Correct arrangement
- User administrator
- Security reader
Explanation
User Administrator is the least-privileged role that grants the ability to create access reviews for groups, as it includes permissions to manage group memberships and identity governance tasks without full admin rights. Security Reader is the least-privileged role that allows User2 to view completed access review history reports, as it grants read-only access to security and compliance reports including access review results without allowing any modifications. Using these roles satisfies the principle of least privilege by avoiding over-permissioned roles like Global Administrator.
Topics
Community Discussion
No community discussion yet for this question.