
SC-300 · Question #133
You have an Active Directory forest that syncs to an Azure Active Directory (Azure AD) tenant. The tenant uses pass-through authentication. A corporate security policy states the following: Domain…
The correct answer is A. Server4. The standalone Authentication Agents can be installed on any Windows Server 2016 or later, with TLS 1.2 enabled. The server needs to be on the same Active Directory forest as the users whose passwords you need to validate…
Question
You have an Active Directory forest that syncs to an Azure Active Directory (Azure AD) tenant. The tenant uses pass-through authentication. A corporate security policy states the following:
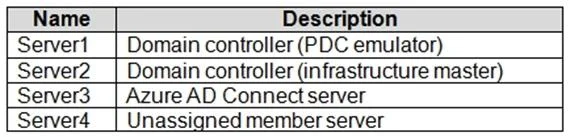
Domain controllers must never communicate directly to the internet. Only required software must be installed on servers. The Active Directory domain contains the on-premises servers shown in the following table. You need to ensure that users can authenticate to Azure AD if a server fails. On which server should you install an additional pass-through authentication agent?
Exhibit
Options
- AServer4
- BServer2
- CServer1
- DServer3
How the community answered
(41 responses)- A76% (31)
- B12% (5)
- C7% (3)
- D5% (2)
Explanation
The standalone Authentication Agents can be installed on any Windows Server 2016 or later, with TLS 1.2 enabled. The server needs to be on the same Active Directory forest as the users whose passwords you need to validate. https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-pta-quick-start
Topics
Community Discussion
No community discussion yet for this question.