
PT0-003 · Question #137
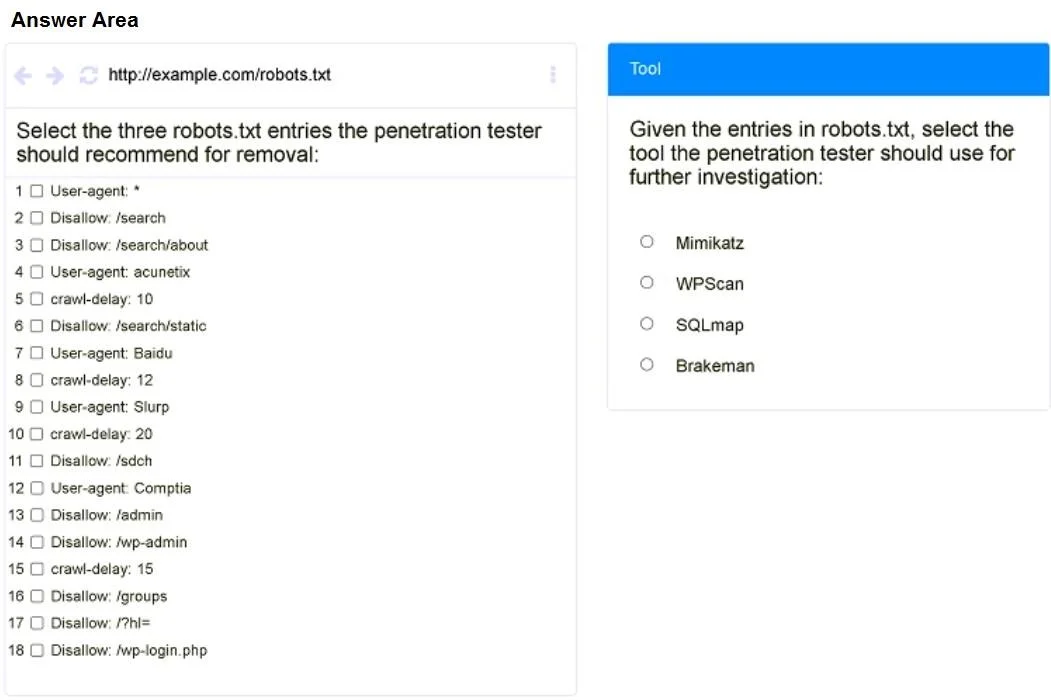
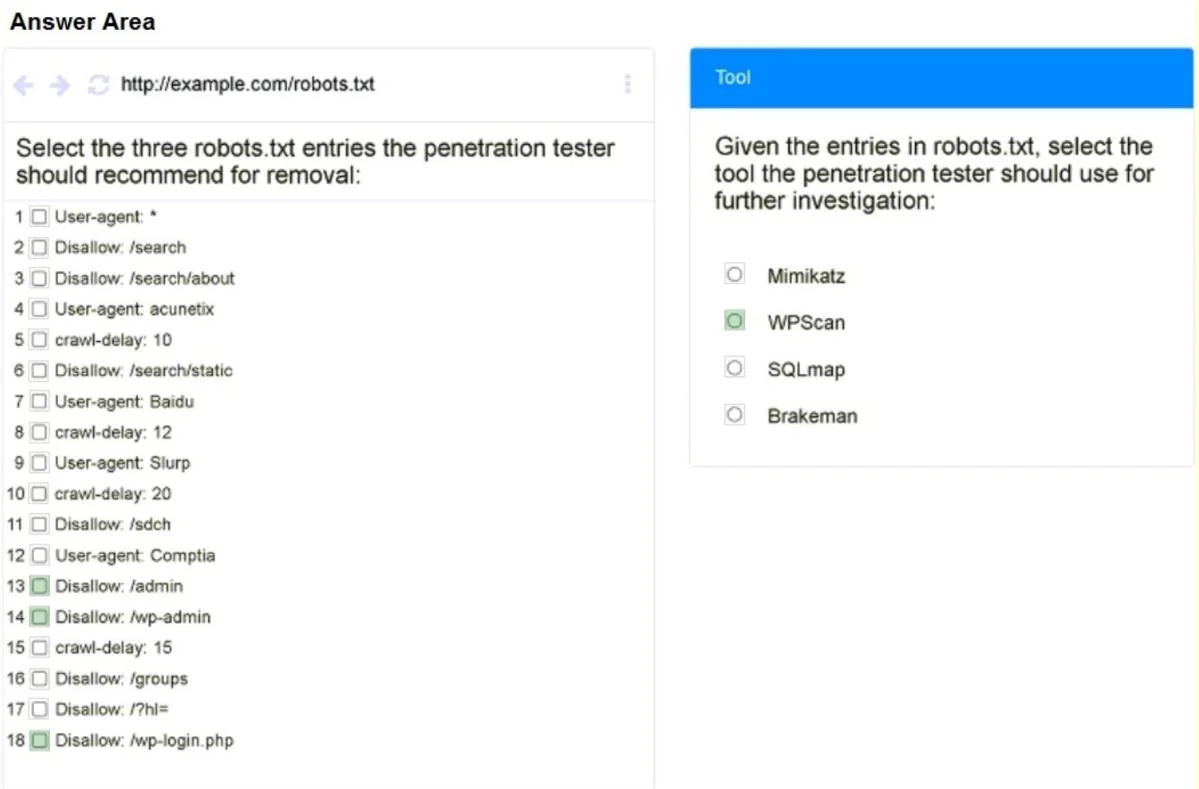
SIMULATION A penetration tester is performing reconnaissance for a web application assessment. Upon investigation, the tester reviews the robots.txt file for items of interest. INSTRUCTIONS Select…
WPScan is the correct tool because the presence of '/wp-login.php' in the robots.txt file reveals the site is running WordPress, making WPScan - a dedicated WordPress vulnerability scanner - the most appropriate tool for further reconnaissance. The entries '/admin' and…
Question
Exhibits
Explanation
WPScan is the correct tool because the presence of '/wp-login.php' in the robots.txt file reveals the site is running WordPress, making WPScan - a dedicated WordPress vulnerability scanner - the most appropriate tool for further reconnaissance. The entries '/admin' and '/wp-login.php' should be recommended for removal because listing them in robots.txt, even as 'Disallow', actually advertises sensitive administrative paths to attackers (robots.txt is publicly readable), making it easier to target login portals and admin interfaces. Removing these entries reduces the attack surface by not explicitly disclosing the existence and location of privileged access points.
Topics
Community Discussion
No community discussion yet for this question.