
PT0-002 · Question #412
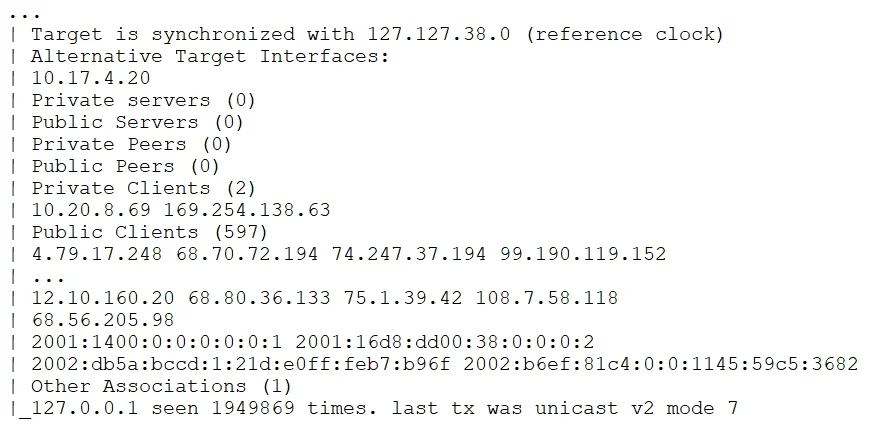
A penetration tester is looking for a particular type of service and obtains the output below: Which of the following commands was executed by the tester?
The correct answer is B. nmap -sU -pU:123-Pn -n --script=ntp-monlist. The output provided indicates the use of the NTP protocol (Network Time Protocol) for querying a target system. The reference to "Public Clients" and the specific IP addresses listed, along with the mention of "Other Associations" and the use of NTP version 2, points towards…
Question
A penetration tester is looking for a particular type of service and obtains the output below:
Which of the following commands was executed by the tester?
Exhibit
Options
- Anmap -sU -pU:517-Pn -n --script=supermicro-ipmi-config
- Bnmap -sU -pU:123-Pn -n --script=ntp-monlist
- Cnmap -sU -pU:161-Pn -n -script=voldemort-info
- Dnmap -sU -pU:37 -Pn -n --script=icap-info
How the community answered
(26 responses)- A4% (1)
- B73% (19)
- C12% (3)
- D12% (3)
Explanation
The output provided indicates the use of the NTP protocol (Network Time Protocol) for querying a target system. The reference to "Public Clients" and the specific IP addresses listed, along with the mention of "Other Associations" and the use of NTP version 2, points towards the execution of an NTP monlist request. The monlist feature in NTP servers can be used to obtain a list of the last 600 hosts that have interacted with the NTP server. The command nmap -sU -pU:123 -Pn -n --script=ntp- monlist <target> specifically targets NTP servers on UDP port 123 to retrieve this information, making it the correct choice based on the output shown.
Topics
Community Discussion
No community discussion yet for this question.