
PT0-002 · Question #153
A penetration tester has been given an assignment to attack a series of targets in the 192.168.1.0/24 range, triggering as few alarms and countermeasures as possible. Which of the following Nmap…
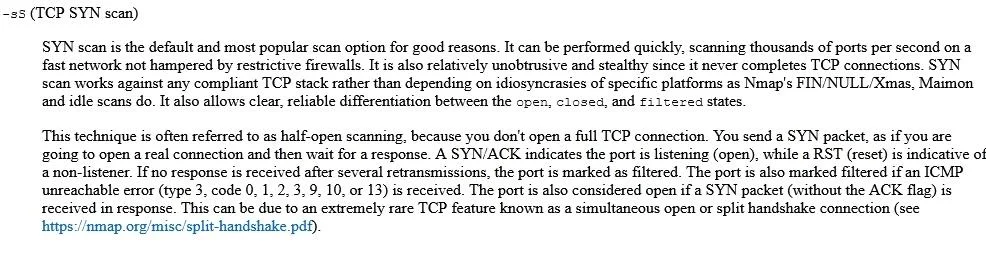
The correct answer is D. nmap -sS -O 192.168.1.2/24 -T1. The goal is stealth - triggering as few alarms as possible. nmap -sS performs a SYN (half-open) scan, which never completes the TCP three-way handshake, making it less likely to be logged by target applications. -T1 sets the timing template to 'Sneaky,' which introduces…
Question
A penetration tester has been given an assignment to attack a series of targets in the 192.168.1.0/24 range, triggering as few alarms and countermeasures as possible. Which of the following Nmap scan syntaxes would BEST accomplish this objective?
Exhibit
Options
- Anmap -sT -vvv -O 192.168.1.2/24 -PO
- Bnmap -sV 192.168.1.2/24 -PO
- Cnmap -sA -v -O 192.168.1.2/24
- Dnmap -sS -O 192.168.1.2/24 -T1
How the community answered
(35 responses)- A11% (4)
- B3% (1)
- C6% (2)
- D80% (28)
Explanation
The goal is stealth - triggering as few alarms as possible. nmap -sS performs a SYN (half-open) scan, which never completes the TCP three-way handshake, making it less likely to be logged by target applications. -T1 sets the timing template to 'Sneaky,' which introduces significant delays between probes, making the scan pattern harder for IDS to detect. -O enables OS detection. Option A uses -sT (full TCP connect, very loud) with -vvv (verbose, no stealth benefit). Option B uses -sV (version detection, aggressive probing). Option C uses -sA (ACK scan for firewall mapping) with no timing control.
Topics
Community Discussion
No community discussion yet for this question.