
PT0-001 · Question #219
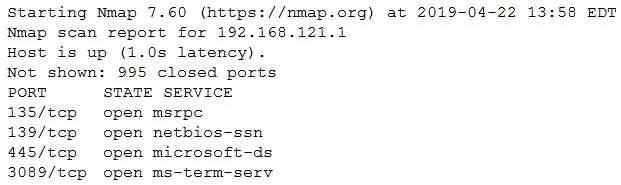
A penetration tester ran an Nmap scan against a target and received the following output: Which of the following commands would be best for the penetration tester to execute NEXT to discover any…
The correct answer is C. snmpwalk -c public 192.168.121.1. After Nmap reveals SNMP port 161 is open, snmpwalk with the default public community string is the best next step to enumerate the full SNMP MIB tree and uncover exploitable information.
Question
A penetration tester ran an Nmap scan against a target and received the following output:
Which of the following commands would be best for the penetration tester to execute NEXT to discover any weaknesses or vulnerabilities?
Exhibit
Options
- Aonesixtyone -d 192.168.121.1
- Benum4linux -w 192.168.121.1
- Csnmpwalk -c public 192.168.121.1
- Dmedusa -h 192.168.121.1 -U users.txt -P passwords.txt -M ssh
How the community answered
(33 responses)- A3% (1)
- B6% (2)
- C76% (25)
- D15% (5)
Why each option
After Nmap reveals SNMP port 161 is open, snmpwalk with the default public community string is the best next step to enumerate the full SNMP MIB tree and uncover exploitable information.
onesixtyone is an SNMP community string brute-forcer used to discover SNMP-enabled hosts and valid community strings; since Nmap already confirmed SNMP is open, scanning for the service again adds no new information.
enum4linux targets SMB and Samba services to enumerate Windows/Linux shares, users, and group policies; it has no relevance when SNMP is the identified open service.
snmpwalk with community string 'public' traverses the entire SNMP MIB tree on the target, extracting system descriptions, interface configurations, running processes, routing tables, and installed software - all of which can reveal exploitable weaknesses or misconfigurations. This directly leverages the service discovered by Nmap to perform deep enumeration without requiring credentials beyond the default community string.
medusa is a brute-force authentication tool and using it against SSH assumes port 22 is the relevant open service, which is not indicated by the Nmap results pointing to SNMP.
Concept tested: SNMP MIB enumeration with snmpwalk after port discovery
Source: http://www.net-snmp.org/docs/man/snmpwalk.html
Topics
Community Discussion
No community discussion yet for this question.