
PT0-001 · Question #20
A security consultant is trying to attack a device with a previously identified user account. Which of the following types of attacks is being executed?
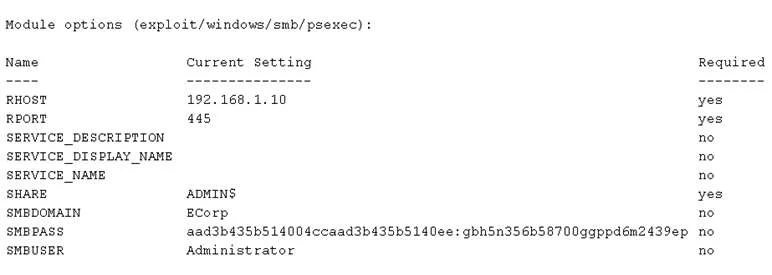
The correct answer is D. Pass the hash attack. In this scenario, the tester is using the Metasploit PSEXEC module. Using Metasploit, a tester can exploit a system and perform a hash dump to extract the systems hashes. The tester can then use the PSEXEC module to pass the hash to another system on the network. The example…
Question
A security consultant is trying to attack a device with a previously identified user account. Which of the following types of attacks is being executed?
Exhibit
Options
- ACredential dump attack
- BDLL injection attack
- CReverse shell attack
- DPass the hash attack
How the community answered
(37 responses)- A3% (1)
- B3% (1)
- C5% (2)
- D89% (33)
Explanation
In this scenario, the tester is using the Metasploit PSEXEC module. Using Metasploit, a tester can exploit a system and perform a hash dump to extract the systems hashes. The tester can then use the PSEXEC module to pass the hash to another system on the network. The example shows how the SMBPASS option is set and the pass-the-hash attack executed, resulting in access to a remote system within the network. A pass-the-hash attack is an exploit in which a tester takes a hashed user credential and, without cracking it, reuses it to deceive an authentication system into creating a new authenticated session on the same network.
Topics
Community Discussion
No community discussion yet for this question.