
NSE5_SSE_AD-7.6 · Question #49
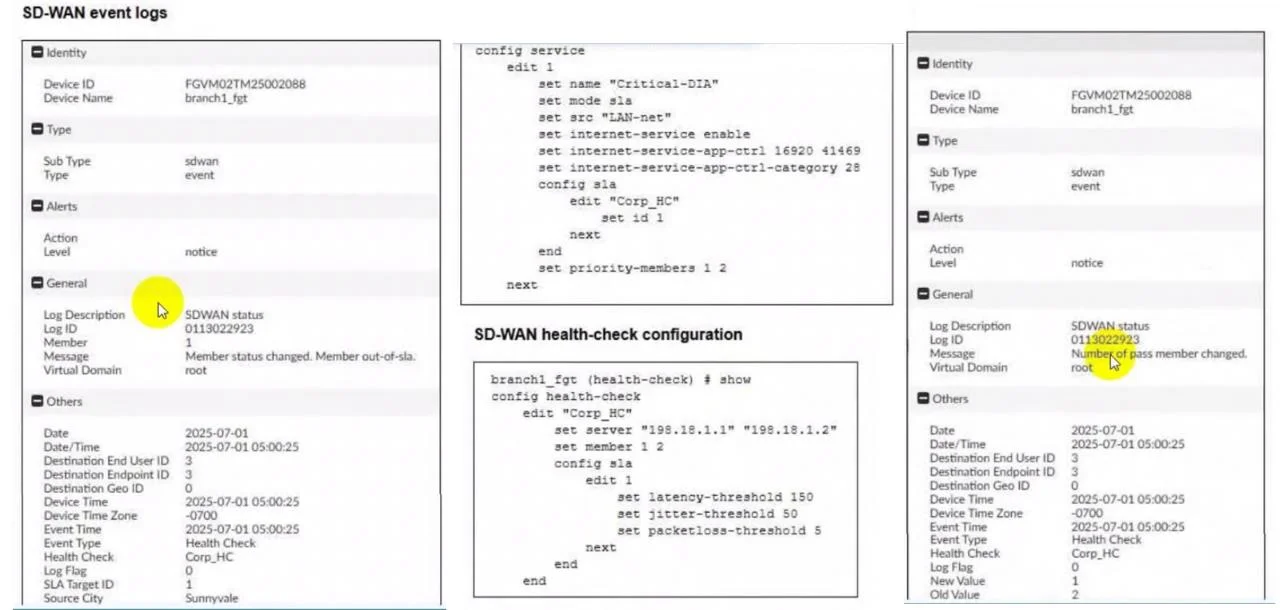
Refer to the exhibits. Two SD-WAN event logs, the member status, the SD-WAN rule configuration, and the health-check configuration for a FortiGate device are shown. Immediately after the log…
The correct answer is C. FortiGate uses port2 to steer the traffic for SD-WAN rule ID 1. According to the SD-WAN 7.6 Core Administrator curriculum and the provided exhibits, the traffic steering decision is determined by the interaction between the Lowest Cost (SLA) strategy and the link health status reported in the event logs. Rule Strategy (Lowest Cost SLA): The…
Question
Refer to the exhibits. Two SD-WAN event logs, the member status, the SD-WAN rule configuration, and the health-check configuration for a FortiGate device are shown. Immediately after the log messages are displayed, how will the FortiGate steer the traffic based on the information shown in the exhibits? (Choose one answer)
Exhibits

Options
- AFortiGate uses port1 or port2 to steer the traffic for SD-WAN rule ID 1.
- BFortiGate uses port1 to steer the traffic for SD-WAN rule ID 1.
- CFortiGate uses port2 to steer the traffic for SD-WAN rule ID 1.
- DFortiGate skips SD-WAN rule ID 1.
How the community answered
(58 responses)- A5% (3)
- B16% (9)
- C69% (40)
- D10% (6)
Explanation
According to the SD-WAN 7.6 Core Administrator curriculum and the provided exhibits, the traffic steering decision is determined by the interaction between the Lowest Cost (SLA) strategy and the link health status reported in the event logs. Rule Strategy (Lowest Cost SLA): The SD-WAN rule configuration for ID 1 (named Critical-DIA) is set to mode sla. In this mode, the FortiGate will only steer traffic through member interfaces that satisfy the assigned Performance SLA targets. Member Preference: The rule defines priority-members 1 2. This means that under normal conditions (where both links are healthy), Member 1 (port1) is the preferred interface because it is Event Log Analysis: The first log message explicitly states: "Member status changed. Member out-of-sla." for Member 1. This indicates that port1 has exceeded one of the thresholds (latency, jitter, or packet loss) defined in the Corp_HC health check. The second log confirms: "Number of pass member changed. New Value: 1, Old Value: 2". This verifies that while there were previously two links passing the SLA, now only one link (Member 2/port2) remains in a passing state. Steering Decision: Because the rule strategy is mode sla and the primary preferred member (port1) is now out-of-sla, the FortiGate immediately disqualifies Member 1 from the selection pool for this specific rule. It then moves to the next available member in the priority list that does satisfy the SLA, which is Member 2 (port2). Exam Questions, Study Guides, Practice Tests. Lead the way to help you pass any IT Certification exams, 100% Pass Guaranteed or Full Refund. Especially Cisco, Microsoft, CompTIA, Citrix, EMC, HP, Oracle, VMware, Juniper, Check Point, LPI, Nortel, EXIN and so on. Our Slogan: First Test, First Pass. Help you to pass any IT Certification exams at the first try. You can reach us at any of the email addresses listed below. Any problems about IT certification or our products, you could rely upon us, we will give you satisfactory answers in 24 hours.
Topics
Community Discussion
No community discussion yet for this question.