
NSE5_SSE_AD-7.6 · Question #40
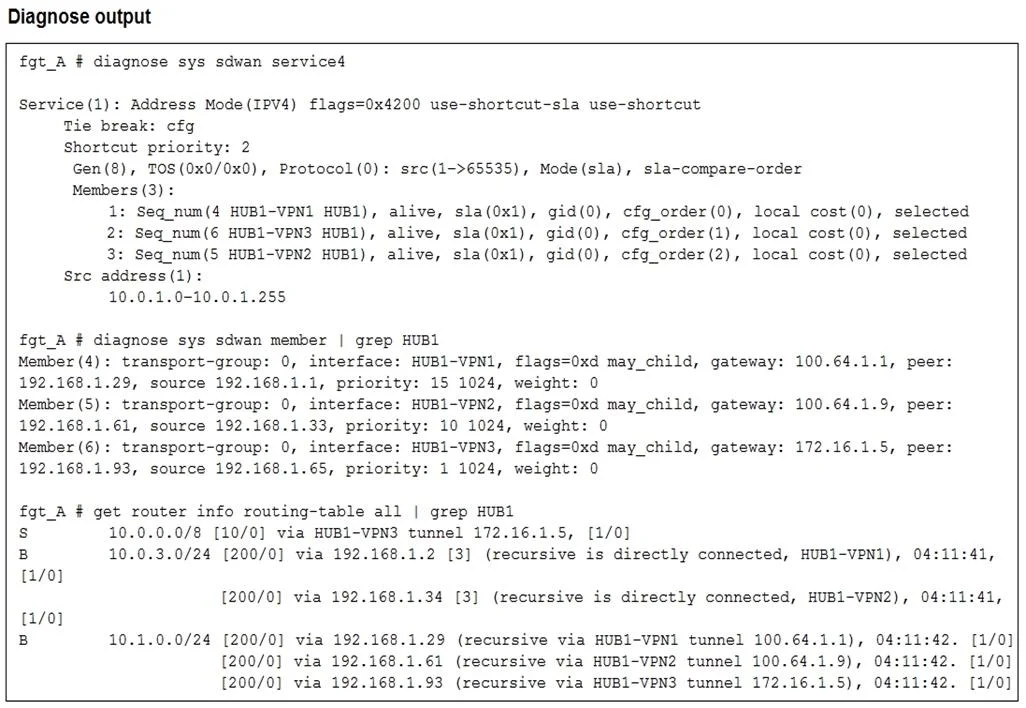
Refer to the exhibit. An administrator is troubleshooting SD-WAN on FortiGate. A device behind branch1_fgt generates traffic to the 10.0.0.0/8 network. The administrator expects the traffic to match…
The correct answer is A. HUB1-VPN1 does not have a valid route to the destination. D. The traffic matches a regular policy route configured with HUB1-VPN3 as the outgoing device. You've hit your limit · resets 5am (America/New_York)
Question
Refer to the exhibit. An administrator is troubleshooting SD-WAN on FortiGate. A device behind branch1_fgt generates traffic to the 10.0.0.0/8 network. The administrator expects the traffic to match SD-WAN rule ID 1 and be routed over HUB1- VPN1. However, the traffic is routed over HUB1-VPN3. Based on the output shown in the exhibit, which two reasons, individually or together, could explain the observed behavior? (Choose two.)
Exhibits

Options
- AHUB1-VPN1 does not have a valid route to the destination.
- BHUB1-VPN3 has a higher member configuration priority than HUB1-VPN1.
- CHUB1-VPN3 has a lower route priority value (higher priority) than HUB1-VPN1.
- DThe traffic matches a regular policy route configured with HUB1-VPN3 as the outgoing device.
How the community answered
(33 responses)- A58% (19)
- B15% (5)
- C27% (9)
Explanation
You've hit your limit · resets 5am (America/New_York)
Topics
Community Discussion
No community discussion yet for this question.