
NSE4_FGT-7.0 · Question #51
Refer to the exhibit. Given the interfaces shown in the exhibit. which two statements are true? (Choose two.)
The correct answer is A. port1-vlan1 and port2-vlan1 can be assigned in the same VDOM or to different VDOMs B. port1 is a native VLAN. The question pertains to FortiGate interface configurations, specifically regarding physical interfaces, VLAN sub-interfaces, and Virtual Domains (VDOMs).
Question
Refer to the exhibit. Given the interfaces shown in the exhibit. which two statements are true? (Choose two.)
Exhibit
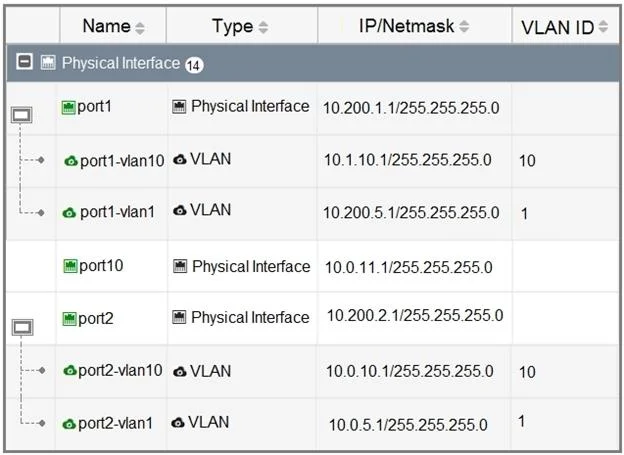
Options
- Aport1-vlan1 and port2-vlan1 can be assigned in the same VDOM or to different VDOMs
- Bport1 is a native VLAN.
- Cport1-vlan10 and port2-vlan10 are part of the same broadcast domain.
- DTraffic between port2 and port2-vlan1 is allowed by default.
How the community answered
(18 responses)- A83% (15)
- C6% (1)
- D11% (2)
Why each option
The question pertains to FortiGate interface configurations, specifically regarding physical interfaces, VLAN sub-interfaces, and Virtual Domains (VDOMs).
VLAN sub-interfaces like port1-vlan1 and port2-vlan1 are distinct logical entities that can be independently assigned to the same VDOM for shared routing contexts or to different VDOMs for multi-tenancy.
When a VLAN sub-interface (e.g., port1-vlan1) is created on a physical port (e.g., port1), the physical port itself acts as the untagged or native VLAN for any traffic not explicitly tagged with a VLAN ID.
VLAN sub-interfaces on different physical ports (e.g., port1-vlan10 and port2-vlan10) are in separate broadcast domains unless explicitly bridged or routed between them.
Traffic between a physical interface (e.g., port2) and its own VLAN sub-interface (e.g., port2-vlan1) is not allowed by default and requires explicit firewall policies or routing configurations for communication.
Concept tested: FortiGate interfaces, VLANs, VDOMs, native VLANs
Source: https://docs.fortinet.com/document/fortigate/7.4.0/fortios-handbook/253683/physical-interfaces-and-vlan-subinterfaces
Topics
Community Discussion
No community discussion yet for this question.