
NSE4_FGT-7.0 · Question #149
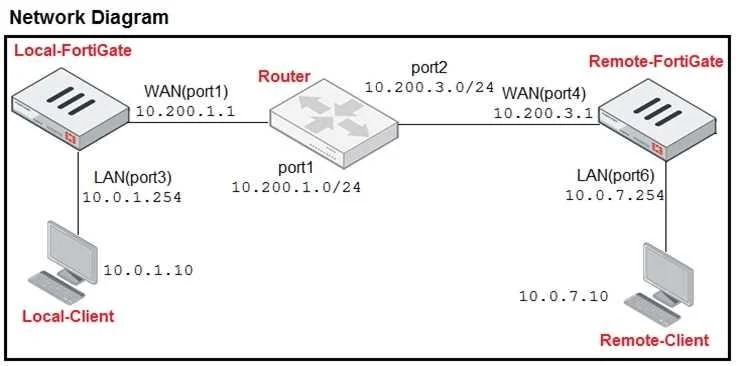
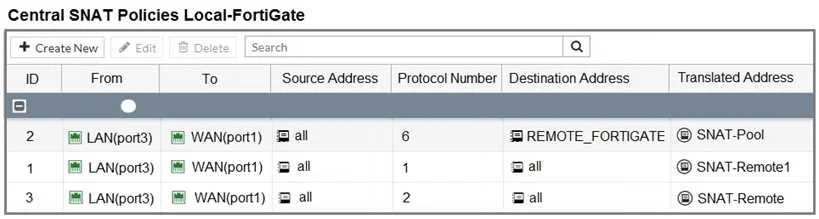
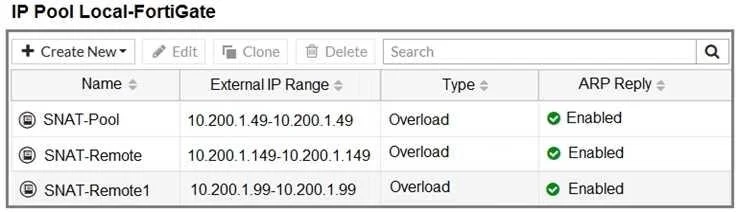
Refer to the exhibit. The exhibit contains a network diagram, central SNAT policy, and IP pool configuration. The WAN (port1) interface has the IP address 10.200.1.1/24. The LAN (port3) interface…
The correct answer is D. 10.200.1.99. With Central NAT enabled and an IP pool configured, the FortiGate will use an IP address from the specified pool for source NAT, which in this case is 10.200.1.99, overriding the outgoing interface IP.
Question
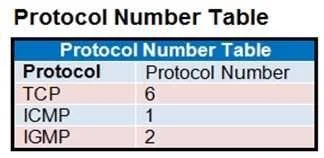
Refer to the exhibit. The exhibit contains a network diagram, central SNAT policy, and IP pool configuration. The WAN (port1) interface has the IP address 10.200.1.1/24. The LAN (port3) interface has the IP address 10.0.1.254/24. A firewall policy is configured to allow to destinations from LAN (port3) to WAN (port1). Central NAT is enabled, so NAT settings from matching Central SNAT policies will be applied. Which IP address will be used to source NAT the traffic, if the user on Local-Client (10.0.1.10) pings the IP address of Remote-FortiGate (10.200.3.1)?
Exhibits
Options
- A10.200.1.149
- B10.200.1.1
- C10.200.1.49
- D10.200.1.99
How the community answered
(18 responses)- B6% (1)
- C11% (2)
- D83% (15)
Why each option
With Central NAT enabled and an IP pool configured, the FortiGate will use an IP address from the specified pool for source NAT, which in this case is 10.200.1.99, overriding the outgoing interface IP.
This IP is an arbitrary address in the WAN subnet and is not specified as the SNAT IP by the provided correct answer or typical FortiGate Central SNAT behavior without explicit configuration in the IP pool.
10.200.1.1 is the WAN interface IP address, which would only be used for SNAT if the Central SNAT policy was configured to 'Use Outgoing Interface Address' instead of an IP pool.
This IP is an arbitrary address in the WAN subnet and is not specified as the SNAT IP by the provided correct answer or typical FortiGate Central SNAT behavior without explicit configuration in the IP pool.
Since Central NAT is enabled and an IP pool is part of the configuration for the Central SNAT policy, the FortiGate will use an IP address from that pool for source NAT, and 10.200.1.99 is the specific address selected from the pool as per the policy.
Concept tested: FortiGate Central SNAT and IP Pool selection
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/607823/central-nat-snat-and-dnat
Topics
Community Discussion
No community discussion yet for this question.