
NSE4_FGT-7.0 · Question #5
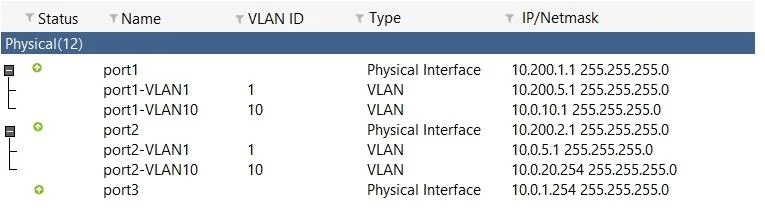
View the exhibit. Which the FortiGate handle web proxy traffic true? (Choose two.)
The correct answer is A. Broadcast traffic received in port1-VLAN10 will not be forwarded to port2-VLAN10. C. port1-VLAN10 and port2-VLAN10 can be assigned to different VDOMs. FortiGate treats VLANs as separate broadcast domains, preventing inter-VLAN broadcast traffic by default, and allows VLAN subinterfaces from the same physical port to be assigned to different VDOMs for strict network segmentation.
Question
View the exhibit. Which the FortiGate handle web proxy traffic true? (Choose two.)
Exhibit
Options
- ABroadcast traffic received in port1-VLAN10 will not be forwarded to port2-VLAN10.
- Bport-VLAN1 is the native VLAN for the port1 physical interface.
- Cport1-VLAN10 and port2-VLAN10 can be assigned to different VDOMs.
- DTraffic between port1-VLAN1 and port2-VLAN1 is allowed by default.
How the community answered
(50 responses)- A82% (41)
- B12% (6)
- D6% (3)
Why each option
FortiGate treats VLANs as separate broadcast domains, preventing inter-VLAN broadcast traffic by default, and allows VLAN subinterfaces from the same physical port to be assigned to different VDOMs for strict network segmentation.
VLANs create distinct broadcast domains; therefore, broadcast traffic originating in port1-VLAN10 will be contained within that VLAN and will not be forwarded by the FortiGate to a different VLAN, such as port2-VLAN10, without explicit routing.
FortiGate does not intrinsically designate a specific VLAN (like VLAN1) as a native VLAN; native VLAN configuration is typically handled on connected network switches.
FortiGate Virtual Domains (VDOMs) provide logical separation of firewall resources. VLAN subinterfaces, even if configured on the same physical port, can be assigned to different VDOMs, enabling complete administrative and traffic isolation between them.
By default, FortiGate firewalls operate on a 'deny-all' principle; traffic between any two interfaces, including different VLANs, is blocked unless an explicit firewall policy is configured to allow it.
Concept tested: FortiGate VLANs, VDOMs, and default policies
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/765089/vlan-subinterfaces
Topics
Community Discussion
No community discussion yet for this question.