
NSE4_FGT-7.0 · Question #21
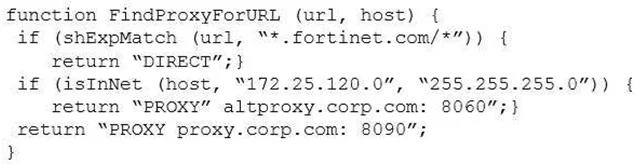
Examine this PAC file configuration. Which of the following statements are true? (Choose two.)
The correct answer is A. Browsers can be configured to retrieve this PAC file from the FortiGate. D. Any web request fortinet.com is allowed to bypass the proxy. PAC files, which can be served by FortiGate, allow browsers to automatically determine proxy usage based on rules, such as bypassing the proxy for specific domains like Fortinet.com.
Question
Examine this PAC file configuration. Which of the following statements are true? (Choose two.)
Exhibit
Options
- ABrowsers can be configured to retrieve this PAC file from the FortiGate.
- BAny web request to the 172.25.120.0/24 subnet is allowed to bypass the proxy.
- CAll requests not made to Fortinet.com or the 172.25.120.0/24 subnet, have to go through
- DAny web request fortinet.com is allowed to bypass the proxy.
How the community answered
(64 responses)- A80% (51)
- B6% (4)
- C14% (9)
Why each option
PAC files, which can be served by FortiGate, allow browsers to automatically determine proxy usage based on rules, such as bypassing the proxy for specific domains like Fortinet.com.
FortiGate devices are capable of hosting and serving PAC (Proxy Auto-Configuration) files via HTTP or HTTPS, allowing client web browsers to be configured to automatically retrieve the PAC file for dynamic proxy settings.
Without the actual PAC file content, it cannot be definitively confirmed that requests to the 172.25.120.0/24 subnet are configured to bypass the proxy, as PAC files are highly customizable to direct such traffic either directly or through the proxy.
The statement's phrasing "All requests not made to Fortinet.com or the 172.25.120.0/24 subnet, have to go through" is problematic because if traffic to 172.25.120.0/24 does not bypass, it would also typically go through the proxy, making the explicit exclusion in the statement potentially incorrect or misleading.
A typical PAC file configuration includes JavaScript rules to determine if traffic should bypass the proxy or use it; a common example is to specify that requests destined for `fortinet.com` (or related subdomains) should be handled directly, bypassing the explicit web proxy.
Concept tested: PAC file configuration and FortiGate interaction
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/468846/explicit-web-proxy-and-profiles
Topics
Community Discussion
No community discussion yet for this question.