
NSE4 · Question #552
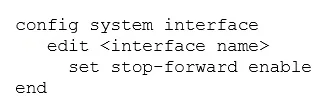
Examine the following interface configuration on a FortiGate in transparent mode: Which statement about this configuration is correct?
The correct answer is B. The FortiGate device forwards received spanning tree BPDU frames. A FortiGate configured in transparent mode acts as a Layer 2 bridge and forwards received Spanning Tree Protocol (STP) Bridge Protocol Data Units (BPDUs) to remain transparent to the network's STP operations.
Question
Examine the following interface configuration on a FortiGate in transparent mode:
Which statement about this configuration is correct?
Exhibit
Options
- AThe FortiGate generates spanning tree BPDU frames.
- BThe FortiGate device forwards received spanning tree BPDU frames.
- CThe FortiGate can block an interface if a layer-2 loop is detected.
- DEthernet layer-2 loops are likely to occur.
How the community answered
(50 responses)- A4% (2)
- B92% (46)
- C2% (1)
- D2% (1)
Why each option
A FortiGate configured in transparent mode acts as a Layer 2 bridge and forwards received Spanning Tree Protocol (STP) Bridge Protocol Data Units (BPDUs) to remain transparent to the network's STP operations.
The FortiGate in transparent mode generally does not generate its own STP BPDU frames unless specifically configured for STP integration; its default behavior is to forward existing BPDUs.
A FortiGate in transparent mode functions as a Layer 2 bridge and, by default, is designed to be invisible to network STP operations by forwarding received STP BPDU frames between connected network segments. This allows the network's STP to operate across the FortiGate as if it were a simple wire.
A FortiGate in transparent mode primarily forwards BPDUs to participate transparently in an existing STP domain; it does not inherently participate in STP to block its own interfaces based on loop detection like a traditional STP-enabled switch.
While layer-2 loops are a general concern in bridged networks, the FortiGate's role in transparent mode (forwarding BPDUs) actually helps prevent loops by allowing the network's STP to function correctly across it, rather than making them more likely.
Concept tested: FortiGate Transparent Mode and STP BPDU Handling
Source: https://docs.fortinet.com/document/fortigate/7.4.0/fortios-administration-guide/575308/transparent-mode
Topics
Community Discussion
No community discussion yet for this question.