
Palo_Alto_Networks
NETSEC-ANALYST · Question #210
View the diagram. What is the most restrictive yet fully functional rule to allow general Internet and SSH traffic into both the DMZ and Untrust/lnternet zones from each of the lOT/Guest and Trust…
Sign in or unlock NETSEC-ANALYST to reveal the answer and full explanation for question #210. The question stem and answer options stay visible for context.
Security Policy Configuration
Question
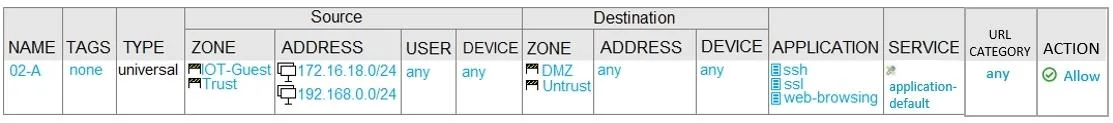
View the diagram. What is the most restrictive yet fully functional rule to allow general Internet and SSH traffic into both the DMZ and Untrust/lnternet zones from each of the lOT/Guest and Trust Zones? A. B. C. D.
Exhibits
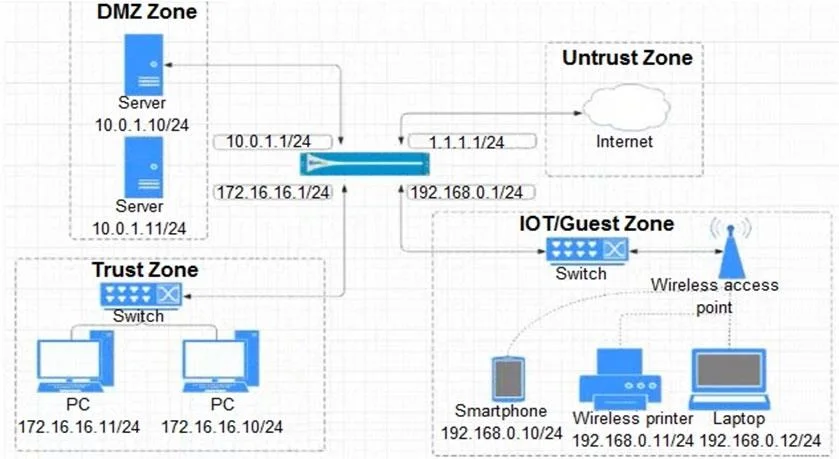
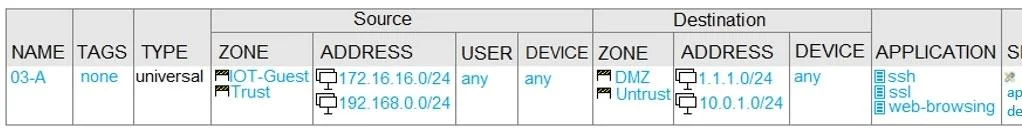
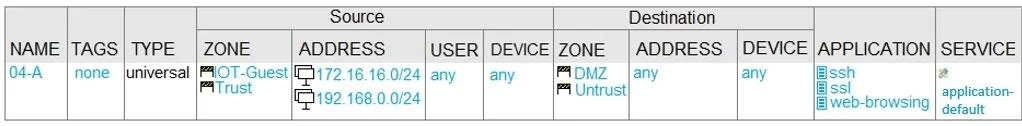
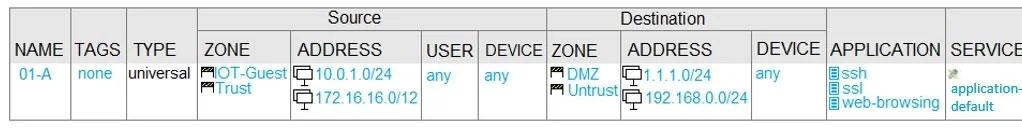
Options
- ASource: NAME: 03-A, TAGS: none, TYPE: universal, ZONE: Trust, ADDRESS: 172.16.16.0/24, 192.168.0.0/24, USER: any, DEVICE: any; Destination: ZONE: DMZ, ADDRESS: 10.0.1.0/24, 1.1.1.0/24, USER: any, DEVICE: any, APPLICATION: ssh, web-browsing, default
- BSource: NAME: 04-A, TAGS: none, TYPE: universal, ZONE: Trust, ADDRESS: 172.16.16.0/24, 192.168.0.0/24, USER: any, DEVICE: any; Destination: ZONE: Untrust, ADDRESS: 1.1.1.0/24, USER: any, DEVICE: any, APPLICATION: ssh, web-browsing, default
- CSource: NAME: 01-A, TAGS: none, TYPE: universal, ZONE: IOT-Guest, ADDRESS: 10.0.1.0/24, 172.16.16.0/12, USER: any, DEVICE: any; Destination: ZONE: DMZ, ADDRESS: 1.1.1.0/24, USER: any, DEVICE: any, APPLICATION: ssh, web-browsing
- DSource: NAME: 02-A, TAGS: none, TYPE: universal, ZONE: IOT-Guest, ADDRESS: 192.168.0.0/24, 172.16.16.0/24, USER: any, DEVICE: any; Destination: ZONE: DMZ, Untrust, ADDRESS: 1.1.1.0/24, USER: any, DEVICE: any, APPLICATION: ssh, web-browsing, default, ACTION: Allow
Unlock NETSEC-ANALYST to see the answer
You've previewed enough free NETSEC-ANALYST questions. Unlock NETSEC-ANALYST for full answers, explanations, the timed quiz mode, progress tracking, and the master PDF. Question stem and options stay visible so you can still see what's on the exam.
Topics
#Security policy rules#zone-based firewall#DMZ#application-based policy