
MS-102 · Question #494
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might…
The correct answer is B. No. Defender for Identity provides three types of security groups: Azure ATP (Workspace name) Administrators, Azure ATP (Workspace name) Users, and Azure ATP (Workspace name) Update Defender for Identity Configuration - Sensors (download, regenerate key, configure, delete) is not…
Question
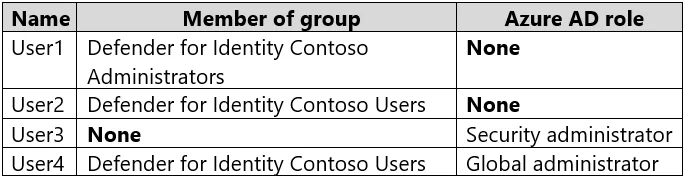
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution. After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen. You have a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com. You create a Microsoft Defender for Identity instance named Contoso. The tenant contains the users shown in the following table. You need to modify the configuration of the Defender for Identity sensors. Solution: You instruct User2 to modify the Defender for Identity sensor configuration. Does this meet the goal?
Exhibit
Options
- AYes
- BNo
How the community answered
(27 responses)- A37% (10)
- B63% (17)
Explanation
Defender for Identity provides three types of security groups: Azure ATP (Workspace name) Administrators, Azure ATP (Workspace name) Users, and Azure ATP (Workspace name) Update Defender for Identity Configuration - Sensors (download, regenerate key, configure, delete) is not available to the "Users" group, only "Admin". https://learn.microsoft.com/en-us/defender-for-identity/role-groups
Topics
Community Discussion
No community discussion yet for this question.