
CS0-003 · Question #123
A security analyst is reviewing a firewall usage report that contains traffic generated over the last 30 minutes in order to locate unusual traffic patterns: Which of the following source IP…
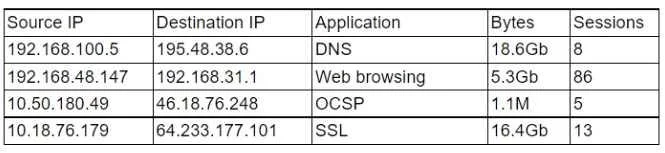
The correct answer is D. 192.168.100.5. The DNS traffic (18.6 GB, 8 sessions) is disproportionately large. Possible reasons: data exfiltration over DNS tunneling, misconfiguration, or malware. This host should be investigated further because its DNS traffic volume is abnormally high for only 8 sessions, suggesting…
Question
A security analyst is reviewing a firewall usage report that contains traffic generated over the last 30 minutes in order to locate unusual traffic patterns:
Which of the following source IP addresses does the analyst need to investigate further?
Exhibit
Options
- A10.18.76.179
- B10.50.180.49
- C192.168.48.147
- D192.168.100.5
How the community answered
(46 responses)- A7% (3)
- B4% (2)
- C15% (7)
- D74% (34)
Explanation
The DNS traffic (18.6 GB, 8 sessions) is disproportionately large. Possible reasons: data exfiltration over DNS tunneling, misconfiguration, or malware. This host should be investigated further because its DNS traffic volume is abnormally high for only 8 sessions, suggesting possible misuse of the DNS protocol for nonstandard data transfer.
Topics
Community Discussion
No community discussion yet for this question.