
CAS-005 · Question #208
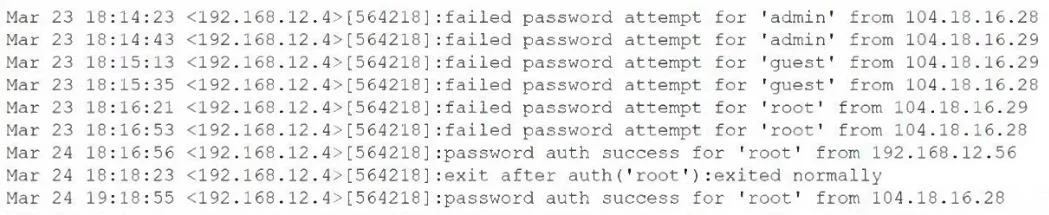
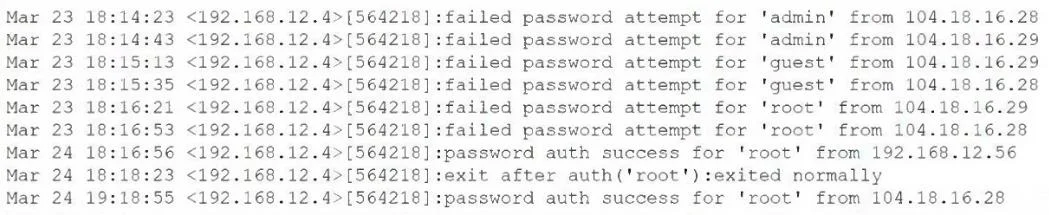
A security operation analyst is reviewing the following log entries for suspicious activity: Which of the following should the analyst do first?
The correct answer is C. Review host 192.168.12.56 for malicious software. Given log entries indicating suspicious activity, the security analyst's most immediate first step should be to investigate the suspected internal host for malicious software.
Question
A security operation analyst is reviewing the following log entries for suspicious activity:
Which of the following should the analyst do first?
Exhibits
Options
- APerform a vulnerability scan on server 192.168.12.4.
- BSearch OSINT on the external IP 104.18.16.29.
- CReview host 192.168.12.56 for malicious software.
- DDisable the guest account on the host 192.168.12.4.
How the community answered
(39 responses)- A3% (1)
- B15% (6)
- C77% (30)
- D5% (2)
Why each option
Given log entries indicating suspicious activity, the security analyst's most immediate first step should be to investigate the suspected internal host for malicious software.
Performing a vulnerability scan on server 192.168.12.4 addresses potential weaknesses but is not the immediate first response to *active suspicious activity* potentially originating from a different compromised host.
Searching OSINT on the external IP 104.18.16.29 is a valuable step for threat intelligence, but the immediate priority is to address and contain the internal threat indicated by suspicious activity on an internal host.
Reviewing host 192.168.12.56 for malicious software is the most appropriate first action because suspicious activity logs often point to a potential compromise of an internal asset. Promptly investigating the host for malware is critical to confirm the compromise and begin containment efforts to prevent further damage or spread.
Disabling the guest account on host 192.168.12.4 is a good security hardening practice but is not the primary first step for responding to active suspicious activity from another internal host, which demands immediate investigation for compromise.
Concept tested: Incident response first steps and triage
Community Discussion
No community discussion yet for this question.