
CAS-005 · Question #209
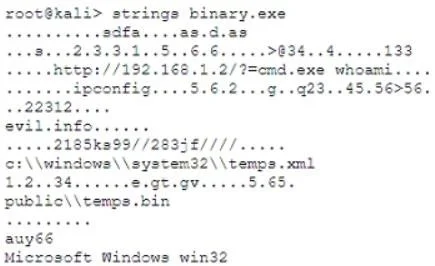
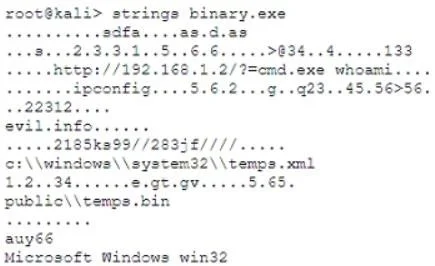
After a cybersecurity incident, a security analyst was able to collect a binary that the attacker used on the compromised server. Then the analyst ran the following command: Which of the following…
The correct answer is B. To extract IoCs from the binary used on the attack. The command strings binary.exe is used to extract human-readable strings from a binary file. This can help the security analyst find indicators of compromise (IoCs), such as IP addresses or commands embedded in the binary. This process aids in identifying critical information…
Question
After a cybersecurity incident, a security analyst was able to collect a binary that the attacker used on the compromised server. Then the analyst ran the following command:
Which of the following options describes what the analyst is trying to do?
Exhibits
Options
- ATo reconstruct the timeline of commands executed by the binary
- BTo extract IoCs from the binary used on the attack
- CTo replicate the attack in a secure environment
- DTo debug the binary to analyze low-level instructions
How the community answered
(21 responses)- A5% (1)
- B76% (16)
- C14% (3)
- D5% (1)
Explanation
The command strings binary.exe is used to extract human-readable strings from a binary file. This can help the security analyst find indicators of compromise (IoCs), such as IP addresses or commands embedded in the binary. This process aids in identifying critical information that can be used for further investigation or remediation of the attack.
Community Discussion
No community discussion yet for this question.