
CAS-005 · Question #150
A security engineer receives an alert from the SIEM platform indicating a possible malicious action on the internal network. The engineer generates a report that outputs the logs associated with the…
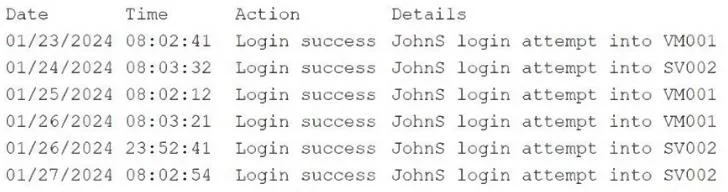
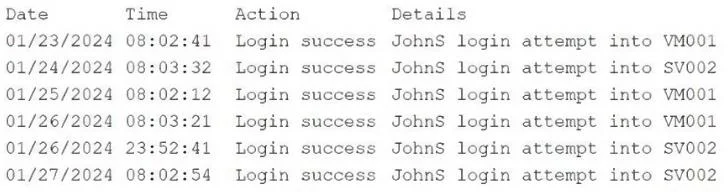
The correct answer is C. Reviewing audit logs from privileged actions. The logs show that JohnS has been logging into different virtual machines (VM001 and SV002), which could indicate suspicious activity, especially if these are sensitive systems. Reviewing audit logs from privileged actions would help the engineer determine whether the logins…
Question
A security engineer receives an alert from the SIEM platform indicating a possible malicious action on the internal network. The engineer generates a report that outputs the logs associated with the incident:
Which of the following actions best enables the engineer to investigate further?
Exhibits
Options
- AConsulting logs from the enterprise password manager
- BSearching dark web monitoring resources for exposure
- CReviewing audit logs from privileged actions
- DQuerying user behavior analytics data
How the community answered
(21 responses)- A5% (1)
- B10% (2)
- C81% (17)
- D5% (1)
Explanation
The logs show that JohnS has been logging into different virtual machines (VM001 and SV002), which could indicate suspicious activity, especially if these are sensitive systems. Reviewing audit logs from privileged actions would help the engineer determine whether the logins are associated with unauthorized actions, changes to critical systems, or other suspicious behavior that might indicate a potential malicious action.
Community Discussion
No community discussion yet for this question.