
AZ-801 · Question #188
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains a user named User1. You deploy a read-only domain controller (RODC) named RODC1. You need to ensure that…
The correct answer is C. Computer Management. To ensure User1 is a local administrator on an RODC while adhering to least privilege, use Computer Management.
Question
Exhibits
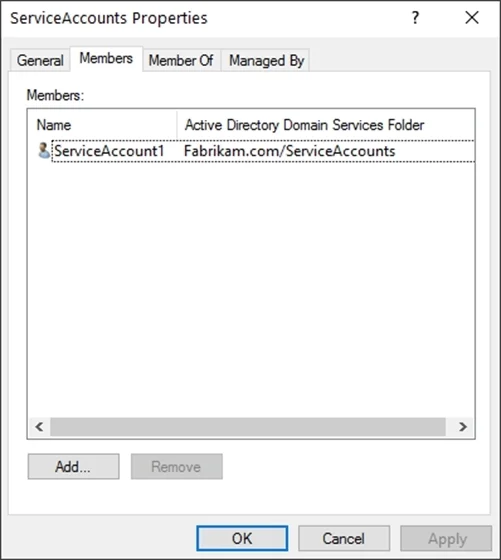
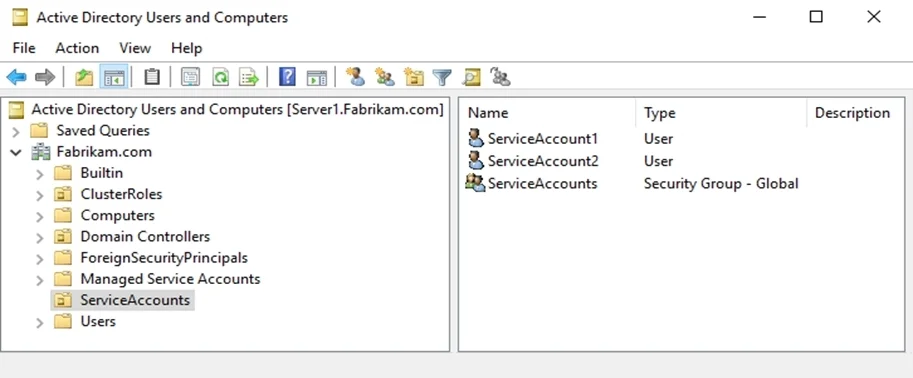
Options
- ASystem Configuration
- Bdsmgmt.exe
- CComputer Management
- DActive Directory Sites and Services
How the community answered
(19 responses)- A5% (1)
- B16% (3)
- C74% (14)
- D5% (1)
Why each option
To ensure User1 is a local administrator on an RODC while adhering to least privilege, use Computer Management.
System Configuration (msconfig.exe) is used for managing system startup options, not for configuring local user group memberships.
dsmgmt.exe is a command-line tool for managing directory service roles and objects, but it is not the primary or most straightforward tool for adding a domain user to a local group on a server with least administrative effort.
Computer Management (compmgmt.msc) provides the 'Local Users and Groups' snap-in, which is the standard graphical interface to manage local group memberships on a Windows Server. This allows you to specifically add User1 to the local Administrators group on RODC1, providing precise control and adhering to the principle of least privilege.
Active Directory Sites and Services is used to manage the AD DS topology, replication, and site-specific settings, not for managing local users and groups on individual servers.
Concept tested: Windows Server local administrator management
Source: https://learn.microsoft.com/en-us/windows-server/identity/ad-ds/deploy/rodc/administering-an-rodc#bkmk_localadmin
Topics
Community Discussion
No community discussion yet for this question.