nerdexam
Microsoft

AZ-305 · Question #68

Case Study 1 - Litware Existing Environment Azure Environment Litware has 10 Azure subscriptions that are linked to the Litware.com tenant and five Azure subscriptions that are linked to the…

This hotspot question tests knowledge of Azure RBAC role scope inheritance, custom role assignability, and Azure AD Conditional Access policies in a hybrid enterprise environment with multiple tenants and subscriptions.

Submitted by andres_qro· Mar 6, 2026Design identity, governance, and monitoring solutions

Question

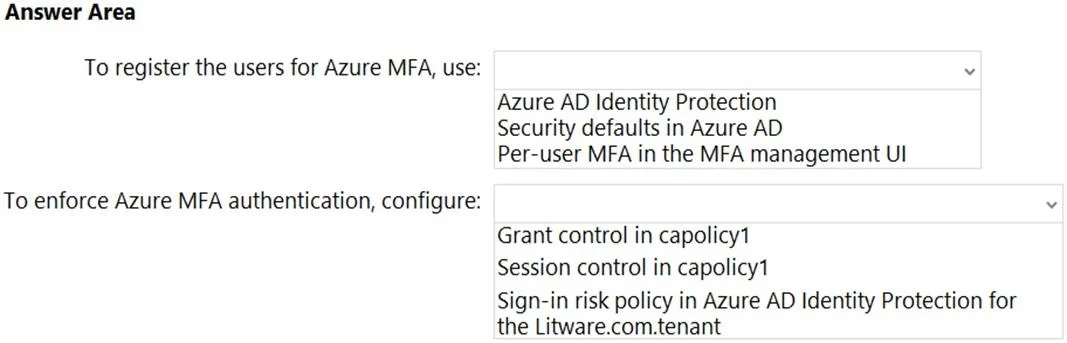
Case Study 1 - Litware Existing Environment Azure Environment Litware has 10 Azure subscriptions that are linked to the Litware.com tenant and five Azure subscriptions that are linked to the dev.litware.com tenant. All the subscriptions are in an Enterprise Agreement (EA). The litware.com tenant contains a custom Azure role-based access control (Azure RBAC) role named Role1 that grants the DataActions read permission to the blobs and files in Azure Storage. On-Premises Environment The on-premises network of Litware contains the resources shown in the following table. Network Environment Litware has ExpressRoute connectivity to Azure. Planned Changes and Requirements Litware plans to implement the following changes: Migrate DB1 and DB2 to Azure. Migrate App1 to Azure virtual machines. Migrate the external storage used by App1 to Azure Storage. Deploy the Azure virtual machines that will host App1 to Azure dedicated hosts. Authentication and Authorization Requirements Litware identifies the following authentication and authorization requirements: Only users that manage the production environment by using the Azure portal must connect from a hybrid Azure AD-joined device and authenticate by using Azure Multi-Factor Authentication (MFA). The Network Contributor built-in RBAC role must be used to grant permissions to the network administrators for all the virtual networks in all the Azure subscriptions. To access the resources in Azure, App1 must use the managed identity of the virtual machines that will host the app. RBAC roles must be applied at the highest level possible. Resiliency Requirements Litware identifies the following resiliency requirements: Once migrated to Azure, DB1 and DB2 must meet the following requirements: - Maintain availability if two availability zones in the local Azure region fail. - Fail over automatically. - Minimize I/O latency. App1 must meet the following requirements: - Be hosted in an Azure region that supports availability zones. - Be hosted on Azure virtual machines that support automatic scaling. - Maintain availability if two availability zones in the local Azure region fail. Security and Compliance Requirements Litware identifies the following security and compliance requirements: Once App1 is migrated to Azure, you must ensure that new data can be written to the app, and the modification of new and existing data is prevented for a period of three years. On-premises users and services must be able to access the Azure Storage account that will host the data in App1. Access to the public endpoint of the Azure Storage account that will host the App1 data must be prevented. All Azure SQL databases in the production environment must have Transparent Data Encryption (TDE) enabled. App1 must NOT share physical hardware with other workloads. Business Requirements Litware identifies the following business requirements: Minimize administrative effort. Minimize costs. Hotspot Question You need to ensure that users managing the production environment are registered for Azure MFA and must authenticate by using Azure MFA when they sign in to the Azure portal. The solution must meet the authentication and authorization requirements. What should you do? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point. Answer:

Exhibits

AZ-305 question #68 exhibit 1
AZ-305 question #68 exhibit 2

Answer Area

  • To register the users for Azure MFA, use:
    Azure AD Identity ProtectionSecurity defaults in Azure ADPer-user MFA in the MFA management UI
  • To enforce Azure MFA authentication, configure:
    Grant control in capolicy1Session control in capolicy1Sign-in risk policy in Azure AD Identity Protection for the Litware.com.tenant

Explanation

This hotspot question tests knowledge of Azure RBAC role scope inheritance, custom role assignability, and Azure AD Conditional Access policies in a hybrid enterprise environment with multiple tenants and subscriptions.

Approach. Role1, defined in the litware.com tenant with DataActions read permissions on blobs and files, can only be assigned within the litware.com tenant's subscriptions - it cannot be assigned in the dev.litware.com tenant because custom RBAC roles are scoped to the tenant where they are created. For the authentication requirement that production environment managers must connect from hybrid Azure AD-joined devices, a Conditional Access policy must be configured targeting the specific users/groups managing production, requiring a compliant or hybrid Azure AD-joined device as a grant condition. ExpressRoute connectivity supports the hybrid environment but does not inherently satisfy Conditional Access requirements - those must be explicitly configured in Azure AD. Custom roles with DataActions are applicable to data plane operations on Storage and cannot grant management plane permissions, meaning Role1 is correctly scoped for blob/file read access but would need separate role assignments for any control plane operations.

Concept tested. Azure RBAC custom role tenant scoping, DataActions permissions for Azure Storage, and Azure AD Conditional Access policies for hybrid Azure AD-joined device requirements in a multi-tenant Enterprise Agreement environment.

Reference. https://learn.microsoft.com/en-us/azure/role-based-access-control/custom-roles and https://learn.microsoft.com/en-us/azure/active-directory/conditional-access/concept-conditional-access-grant

Topics

#Azure MFA#Conditional Access#identity security#Azure AD Identity Protection

Community Discussion

No community discussion yet for this question.

Full AZ-305 Practice