
AZ-305 · Question #116
Hotspot Question You need to design an Azure policy that will implement the following functionality: - For new resources, assign tags and values that match the tags and values of the resource group…
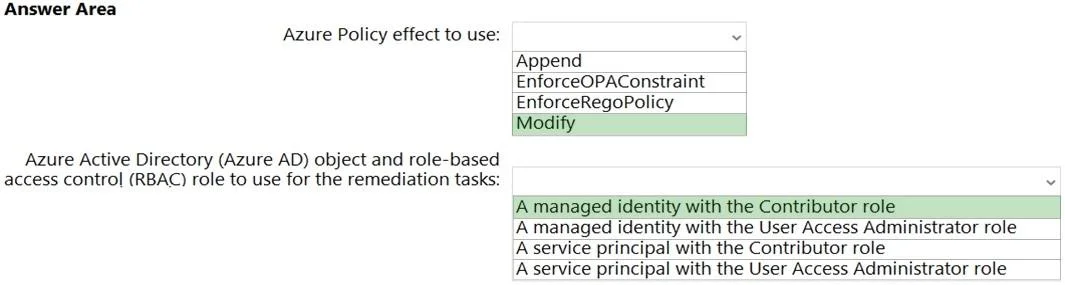
The correct answer is Azure Policy effect to use:: Modify; Azure Active Directory (Azure AD) object and role-based access control (RBAC) role to use for the remediation tasks:: A managed identity with the Contributor role. This question tests knowledge of Azure Policy effects and the appropriate RBAC role required to implement tag inheritance with auto-remediation using the principle of least privilege.
Question
Exhibit
Answer Area
- Azure Policy effect to use:ModifyAppendEnforceOPAConstraintEnforceRegoPolicyModify
- Azure Active Directory (Azure AD) object and role-based access control (RBAC) role to use for the remediation tasks:A managed identity with the Contributor roleA managed identity with the Contributor roleA managed identity with the User Access Administrator roleA service principal with the Contributor roleA service principal with the User Access Administrator role
Explanation
This question tests knowledge of Azure Policy effects and the appropriate RBAC role required to implement tag inheritance with auto-remediation using the principle of least privilege.
Approach. The correct policy effect to use is 'Modify', because the Modify effect can add, update, or replace tags on resources during creation/update (for new resources) AND can be used with remediation tasks to fix existing non-compliant resources. The built-in policy 'Inherit a tag from the resource group if missing' uses the Modify effect. For the managed identity used by the remediation task, the least privileged role is 'Contributor' - specifically, the 'Tag Contributor' role (which is a built-in role granting rights to manage tags without full resource access), satisfying the principle of least privilege. The managed identity associated with the policy assignment must be assigned the Tag Contributor role so it can apply tags to non-compliant resources without having broader permissions. The compliance evaluation identifies existing non-compliant resources, and the Modify effect with a remediation task triggers auto-generated remediation to bring those resources into compliance.
Concept tested. Azure Policy effects (Modify vs Append vs DeployIfNotExists), RBAC roles for policy remediation managed identities (Tag Contributor for least privilege), and how Modify effect enables both new resource tag assignment and remediation task creation for existing non-compliant resources.
Reference. https://docs.microsoft.com/en-us/azure/governance/policy/concepts/effects#modify and https://docs.microsoft.com/en-us/azure/governance/policy/how-to/remediate-resources
Topics
Community Discussion
No community discussion yet for this question.