
350-501 · Question #563
Refer to the exhibit. The company is running IS-IS in its core-A network engineer must segment the network into two areas to isolate departments. However, some networks must be shared from area 2 to…
The correct answer is B. Implement route-tagging on RB and RD to identity and allow only the routes that should be. To segment an IS-IS network into two areas while selectively sharing routes, the engineer should implement route-tagging on the Level 1/Level 2 boundary routers (RB and RD) to identify and permit only the desired routes between areas.
Question
Refer to the exhibit. The company is running IS-IS in its core-A network engineer must segment the network into two areas to isolate departments. However, some networks must be shared from area 2 to area 1 so the engineer has decided to implement route filtering between devices. Which action must the engineer take so that the correct networks are shared between IS-IS areas?
Exhibit
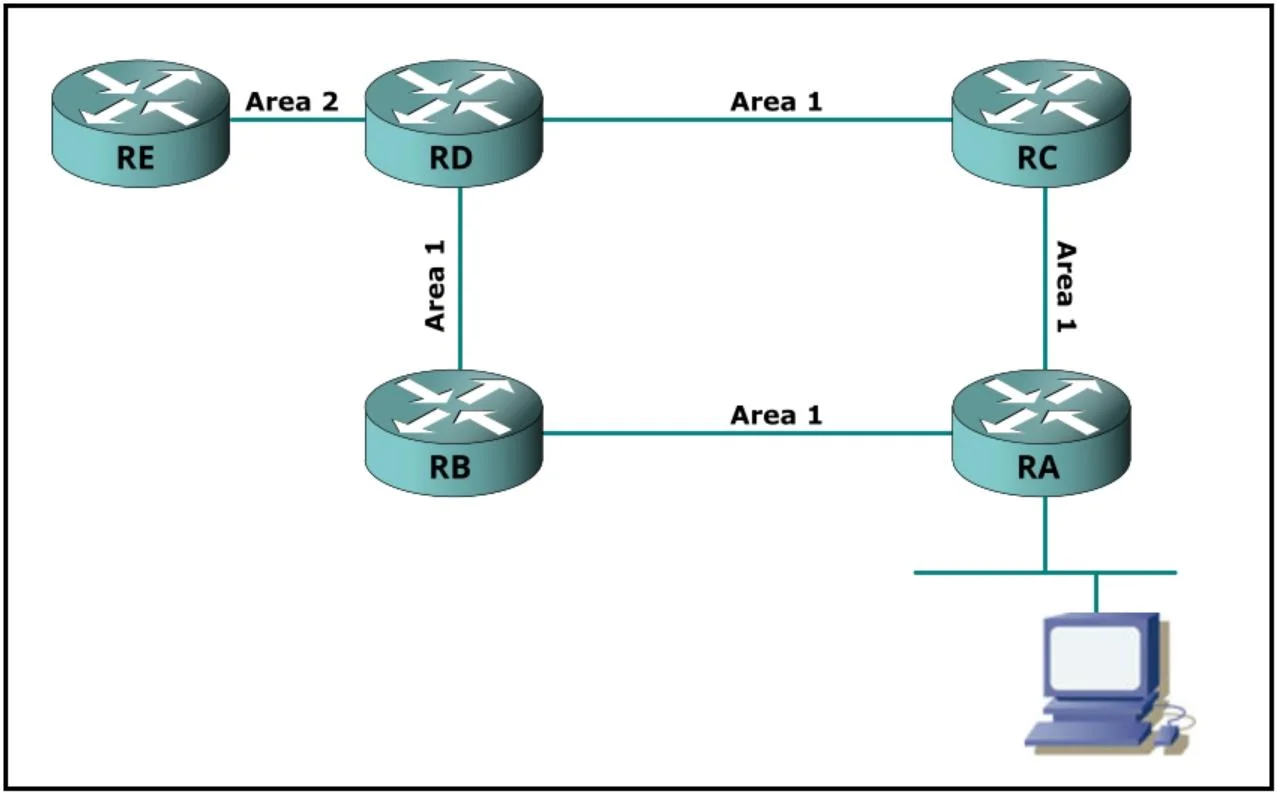
Options
- AImplement a route map and attach it to a distribute list on RD to filter inbound routes from RE.
- BImplement route-tagging on RB and RD to identity and allow only the routes that should be
- CSet a unique area ID on each router to fully segment the network.
- DApply an ACL on RE to deny unnecessary routes from exiling the interface toward RD.
How the community answered
(44 responses)- A14% (6)
- B73% (32)
- C5% (2)
- D9% (4)
Why each option
To segment an IS-IS network into two areas while selectively sharing routes, the engineer should implement route-tagging on the Level 1/Level 2 boundary routers (RB and RD) to identify and permit only the desired routes between areas.
While route maps and distribute lists can filter inbound routes, route-tagging provides a more robust and scalable solution for inter-area route control in IS-IS, especially for specific route sharing.
In IS-IS, route-tagging is a common and effective method to control route advertisement between Level 1 and Level 2 areas, especially when summarization or simple filtering isn't sufficient. By tagging routes at the L1/L2 boundary routers (like RB and RD) in one area, these tags can then be used in route-maps on the boundary routers of the other area to filter which routes are redistributed, ensuring only specific networks are shared.
Setting a unique area ID on each router is standard for IS-IS operation, but it only defines the areas and does not inherently implement selective route sharing or filtering between them.
Applying an ACL on an interface to deny unnecessary routes is a generic filtering method, but route-tagging, coupled with route maps, offers more granular control and is a best practice for inter-area route policy in IS-IS.
Concept tested: IS-IS inter-area route filtering with route-tagging
Source: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/iproute_isis/configuration/15-mt/irs-15-mt-book/irs-route-filter-sum.html
Topics
Community Discussion
No community discussion yet for this question.